Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

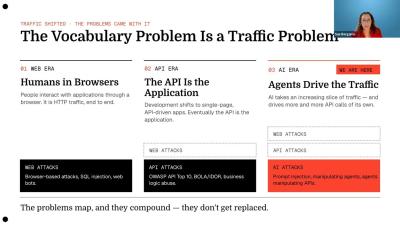
WAF vs WAAP API vs AI What Security Tools Do You Actually Need?

A straightforward framework for matching each layer of protection to the problem it actually solves. Trying to understand vendors in the modern application security space can feel a lot like trying to solve word scramble. Whether it’s remembering what the “A’s” in "WAAP” stand for, figuring out if “WAF” includes APIs, or assessing the actual function of a new AI security product, understanding what tools your team actually needs is getting harder all the time.
The New CISO Ep. 151 - Sean Murphy | Complacency Kills: Why More Discomfort Might Fix Your Burnout

Sean Murphy spent more than twenty years in the CISO chair and walked away from it while things were going well. In this episode of The New CISO, he returns to talk with Steve Moore about trading the operational seat for a field CISO role at F5 — and why getting too good at the job was the warning sign.

Tanium Provision, "Bare Metal in 2026": Tanium Tech Talks #171

Tanium Provision takes a device from bare metal to domain-joined and software-ready, hands-off, from start to finish. This episode walks through the entire process, end to end. Rob Broughall takes us through the full provisioning journey: setting up the infrastructure, building a Windows 11 bundle from the ground up, and watching a device go from bare metal to domain-joined and running software in under two hours.

Claude Mythos Explained: AI Finding Zero-Day Vulnerabilities and Chaining Exploits

Claude Mythos is an AI model capable of finding and chaining zero-day vulnerabilities at scale. That changes how attacks happen, especially in environments where you can’t patch fast enough. The Forescout Vistaro platform with VistaroAI helps organizations respond with real-time visibility and dynamic control across all connected devices.

How to Evaluate and Choose the Best GRC Software in 2026

Evaluating GRC software in 2026? Every platform says it covers governance, risk, and compliance. What a demo will not show you is whether it runs on one connected system or a stack of separate tools sharing a single login, and that difference decides whether you can answer leadership on the spot or spend a week rebuilding the picture. This video walks through five criteria for judging any GRC platform, and the question to ask a vendor on each one.

DPDP Readiness for Indian Businesses From Compliance Requirements to Data Protection

India’s Digital Personal Data Protection (DPDP) framework is changing how businesses need to manage and protect personal data. In this video we explore what DPDP readiness means in practice and how organizations can strengthen their approach to protecting personal data throughout its lifecycle. The session covers: The webinar also discusses how backup and recovery capabilities can support a broader data-protection and compliance strategy, including encryption, access control, immutable storage, policy-based retention, centralized management, and recovery.

When Cybersecurity Becomes Pay to Play

Awards you have to pay to win, events you have to pay to attend and conferences that expect speakers to work for free. When did recognition and expertise in cybersecurity become something you have to buy? Welcome to Razorwire, the podcast where we share our take on the world of cybersecurity with direct, practical advice for professionals and business owners alike. I'm Jim and in this episode I'm joined by security consultant and regular community speaker James Bore and Gary Hibberd, co-founder of Consultants Like Us and the Real Cyber Awards and Conference.

Session on Air-Gapped AI: Architecture, Challenges and Best Practices at GISEC Global 2026

In this Session at GISEC Global 2026, Dubai Exhibition Centre (DEC), Expo City, our Founder & CEO, Mr. Anirban Mukherji, discussed the importance of balancing AI innovation, data sovereignty, privacy, and national security in the era of frontier Large Language Models.

Build from source with Matt Moore from Chainguard | Zero-Shot Learning

In 2020, the SolarWinds attack exposed the vulnerability of supply chains worldwide, a problem this episode’s guest, Matt Moore, had already been working to solve for years. In 2021, he co-founded Chainguard to protect supply chains from future breaches. His conversation with 1Password CTO Nancy Wang and Google Gemini’s Dev Tagare covers why the open source trust model is structurally broken and how AI agents have complicated supply chain security, with a live demo demonstrating how standard tools overlook many vulnerabilities.