Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

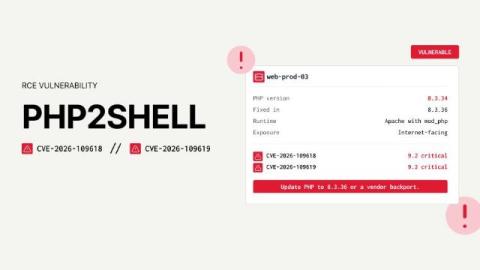
PHP2Shell: Responding to CVE-2026-109618 and CVE-2026-109619

If you run PHP anywhere in your environment, patch to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35 now. Two critical flaws disclosed this week, CVE-2026-109618 and CVE-2026-109619 (nicknamed "PHP2Shell"), let an unauthenticated attacker run code on a server with nothing more than a crafted web request. Both carry a CVSS v4.0 score of 9.2, every earlier release is affected, and exploitation in the wild has been reported. The patch is the easy part.
AI Compute Just Became an Endpoint Problem

For the last three years, enterprise AI happened somewhere else. Models trained in someone’s cloud, inference ran behind an API, and the endpoint stayed where it had always been: on a laptop that opened a browser. With local AI computing platforms like NVIDIA DGX Spark (opens in a new tab), RTX Spark (opens in a new tab), and DGX Station (opens in a new tab), that framework is ending.

CrowdStrike Uncovers New Agentic AI Campaigns

A new report from the CrowdStrike Counter Adversary Operations team details research into four previously unreported threat actors, each of whom left their offensive agent frameworks exposed via open directories. In doing so, they shared detailed insight into their use of AI agents and revealed how adversaries are quickly becoming more proficient in AI.

CrowdStrike Protects Customers from Threats Delivered via PHP2Shell

Two critical memory-corruption remote code execution (RCE) vulnerabilities, collectively dubbed PHP2Shell, have been disclosed in core PHP, the underlying engine powering a vast portion of the web. The CrowdStrike Falcon platform provides out-of-the-box visibility and detection coverage for post-exploitation activities of both vulnerabilities.

Building the Business Case for Agentic AI Security Investment

Security investment decisions are always, at some level, conversations about risk quantification: how much exposure does the organization actually carry, what does it cost to reduce that exposure, and what's the cost of not acting at all. For agentic AI security, these questions are answerable once the right measurement is in place.

Protecting sovereign AI with CloudCasa and SUSE AI Factory

A production AI service accumulates data that your team needs to recover: documents, embeddings, vector indexes, application settings, and conversation history. Once a retrieval-augmented generation (RAG) pipeline connects a model to your organization’s information, those dependencies become part of the service you operate. SUSE and CloudCasa by Catalogic are working together to protect that state in SUSE AI Factory.

What you need to know about PHP2shell. Critical vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619)

Two critical remote code execution vulnerabilities have been found in PHP itself. Treat all versions as affected. ‍The vulnerabilities, CVE-2026-109618 and CVE-2026-109619, both have a CVSS v4.0 score of 9.2. The PHP security team will release fixes on October 21, 2026, at 16:00 CEST / 10:00 EDT / 07:00 PT. If you run PHP anywhere in your stack, please stay tuned for workarounds and patches. Be prepared to take action.
Featured Post

How do you prepare leaders for a security crisis?

Toro Solutions and Insignia Crisis Management recently brought together people experienced in security, crisis management, communications and resilience to discuss how to prepare leaders for a serious security crisis. Most organisations work to prevent serious security incidents and plan how to respond. But a plan can only take you so far. People must make decisions quickly, with incomplete information, while the situation is still changing.

The Benefits of Segmenting Visitor Wireless Access from Corporate Networks

Convenient internet access is available to visitors through guest Wi-Fi without granting them entry into internal systems. Risks to digital safety are present when guests utilize the same infrastructure as corporate computers and servers. Partitioning these connections is a method to safeguard private data and ensure consistent connection speeds. Network isolation is a functional component of a security plan for organizations that host clients or contractors.

When the Breach Already Happened: Choosing a Security Team That Earns Its Keep

Managed cybersecurity services turn a scattered pile of security tools into one accountable team that watches your systems while your own staff sleeps, ships product, or simply steps away from the desk. The promise is quiet but powerful. Someone competent is always on duty, confirmed threats get contained in minutes rather than days, and the monthly bill lands well below the cost of staffing three analyst shifts yourself.