Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

AI Is Calling In Every Risk You've Accepted: Seven Insights From The AI Security Panel: Unfiltered

On October 14th, the afternoon before the AI Security Summit (AISS) flagship event in San Francisco, Snyk hosted The AI Security Panel: Unfiltered. Yahoo Finance's Deirdre Bosa moderated four people who see AI security from very different seats.

How to build a CPS 230-aligned TPRM program

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Scanning AI Assets: Catching What SCA and SAST Might Miss

Your standard application security tools are designed to protect your software pipeline by checking third-party components for known vulnerabilities (via SCA), analyzing source code for security flaws (via SAST), and scanning for accidentally exposed credentials (using secret scanners). But if a developer drops a SKILL.md file into their coding agent, installs a plugin from a marketplace, or pulls in an APM manifest, your AppSec scanners may not catch it.

Shadow AI Detection Now Extends to Developer Workstations

ZIP files shared between co-workers containing new agent skills, locally-developed MCP servers passed between developers, and locally stored newly-minted agents are all seemingly harmless files that are commonly used in corporate software development environments. Unfortunately, far from being harmless, these locally stored files can contain AI assets that were never detected or registered as an approved artifact in your applications.

Arctic Wolf Labs: Finding, Prioritizing, and Patching PHP2Shell Exposure

On Tuesday, October 20, threat actors gained advance visibility into two critical PHP vulnerabilities after details leaked ahead of the planned disclosure, accelerating the race between defenders and attackers. The flaws are tracked as Common Vulnerabilities and Exposures (CVE) identifiers CVE-2026-109618 and CVE-2026-109619. Together they’re known as PHP2Shell. Both carry a 9.2 rating on the Common Vulnerability Scoring System (CVSS) version 4.0 scale.

Immutable Backup: What It Protects, and What It Doesn't

An immutable backup is a copy of data that cannot be modified or deleted for a defined retention period, by anyone, including an administrator with full privileges. The retention period is set when the data is written and enforced by the storage layer rather than by permissions, which is what makes it different from a backup that is merely protected by access control. The reason it matters is narrow and important.

Proving the Value of Threat Intelligence in 2027: Metrics the Board Will Understand

Cyber attacks on UK retailers and manufacturers have shown boards that cyber risk is business risk. This blog explains why the whole organisation needs to understand the value of threat intelligence, and sets out the metrics that translate intelligence into language the board understands: money, time, exposure and reputation.

Cloudflare Responds to Critical PHP RCE Vulnerabilities: Why WAF Enforcement Matters

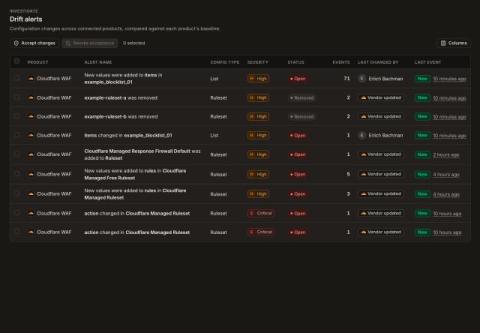
Two critical PHP vulnerabilities have been disclosed, potentially exposing millions of web servers to remote code execution. Cloudflare has already responded by deploying emergency WAF protections. For Reach customers using Cloudflare WAF, Reach Drift automatically detected the new rules and confirmed they were enabled and configured to block malicious traffic.

CVE-2026-94244: Missing Authorization in Wallet System for WooCommerce

Vulnerability: Missing Authorization Leading to Store-Wide Customer Data Exposure via Exported Wallet Transaction File Vulnerable Version: < 2.8.0 Patched Version: 2.8.0 CVE: CVE-2026-94244 CVSS: 4.3 (Medium) AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:N CWE: CWE-862 (Missing Authorization) → CWE-200 (Sensitive Information Disclosure) On 02/09/2026, a security researcher at Astra Security found a Missing Authorization vulnerability in Wallet System for WooCommerce, a popular WordPress plugin by WP Swings that