Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

CISO Risk Intel Brief: Trusted Ingress, Edge Zero-Days, and AI-Generated Code Define Residual Risk

This briefing covers material developments for the seven-day period of 14–21 October 2026 and the thirty-day period of 21 September–21 October 2026. It is written for board risk committees, peer CISOs, and security leadership. The focus is residual risk, control effectiveness, and business enablement across application security, software supply chain, cloud and infrastructure, identity, third-party exposure, and AI-assisted development.
Smaller Models for Better Document Understanding

At Cyberhaven, we replaced our previous LLM-based approach to document understanding with a small model that makes 83% fewer decision errors at less than 1% of the inference cost. We achieved this by breaking complex tasks into simpler decisions, using uncertainty as a training signal, and heavily optimizing our inference stack. The model produces calibrated decision probabilities while preserving multimodal understanding and generative capabilities.

LiteLLM compromised again: infostealer and RAT found in version 1.107.0

On October 21, 2026, version 1.107.0 of LiteLLM (a popular open source proxy that lets developers route requests across dozens of LLM providers) was found to be compromised by an attacker who injected malicious code into its published Python wheels on PyPI. The official Docker image for the same version is also compromised.

Cloudflare deploys protections against php2shell vulnerability

Today, Calif.io, Wiz, OpenAI and Quarkslab disclosed two vulnerabilities in PHP, tracked as CVE-2026-109618 and CVE-2026-109619 and known as php2shell. The vulnerabilities affect all web servers running PHP 5.4 or later and they may allow an attacker to cause denial of service, remote code execution, and data exposure when an application processes specially crafted HTTP traffic.

Introducing full transaction detection for Cloudflare WAF

Today, we are expanding our web application firewall (WAF) by adding two new capabilities: full transaction detections and response rules. Full transaction detections evaluate each HTTP request alongside its response to identify evidence of exploitation. It helps answer both "Does this request look malicious?" and "What happened when the application handled it?" Response rules can then block the origin’s response before it reaches the requester.

Building "php2shell" detections before coordinated disclosure

We recently collaborated with OpenAI, PHP, and a number of other organizations to respond to a pair of serious remote code execution vulnerabilities in PHP that are likely to impact the majority of the world's public web servers. PHP underpins a large part of the web, powering content management systems, online stores, and business applications. Its security matters to vital services that millions of people and organizations rely on daily.

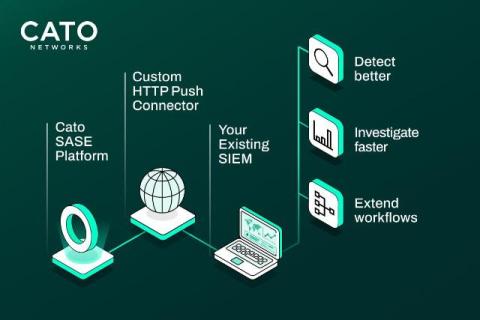
Make Your SIEM Smarter with Cato

Effective security operations require more than isolated alerts. Analysts need context from across the environment to understand what happened, assess its significance, and decide what to do next. That is why accessing insights and telemetry from across your networking and security stack is critical to teams using a SIEM tool.

Critical PHP Vulnerabilities (CVE-2026-109618 & CVE-2026-109619)

On October 20, 2026, the PHP security team issued an advance security advisory regarding two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, affecting core PHP source code. Both vulnerabilities carry a critical-severity CVSS v4.0 score of 9.2 and could potentially allow unauthenticated remote code execution (RCE) on affected servers. The official patched PHP releases are now available.

CertKit now has 86 built-in deployment templates

There are lots of ways to get a certificate. Getting it onto your Cisco ISE, IBM i, or WatchGuard VPN is the hard part. We keep making that easier. Since July, CertKit has added 51 new deployment templates, more than doubling the library to 86. Each platform has a built-in deployment template, and most have a deployment guide for the setup details. Setup is just picking a certificate and setting a few variables.