Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

The post-quantum EO is an important milestone. Now it's time to get to work

On June 22, 2026, President Trump signed Executive Order 14409, "Securing the Nation Against Advanced Cryptographic Attacks." The order sets a December 31, 2030, deadline for federal agencies to transition their most sensitive systems to post-quantum encryption, and a December 31, 2031, deadline for post-quantum authentication. The EO also directs federal contractors to comply with post-quantum Federal Information Processing Standards (FIPS) by the end of 2030.
Top Software Supply Chain Security Best Practices for Enterprises

If an attacker compromised a dependency buried three levels deep in your build pipeline tonight, how long would it take you to find out? Open source libraries, third-party frameworks, transitive dependencies, build tooling, and now AI-generated code that developers may not have reviewed line by line: each of these components flows into your application, whether your team explicitly chose it or not. Each component is a potential entry point.

Blocking USB Devices and Whitelisting Authorized Peripherals with DLP

Data Loss Prevention (DLP) is all about keeping your business data safe from getting leaked, lost, or accessed without admin permission. It protects, identifies, analyzes, and blocks unauthorized data transfers within the network and through connected devices and outbound emails. DLP enforces company policies, preventing users from sharing confidential information. It further allows organizations to set USB restrictions to protect sensitive information at every stage of operations.

DPDP Rules, 2025: A Guide to Digital Personal Data Protection

The notification of the Digital Personal Data Protection (DPDP) Rules, 2025, marks a major turning point in how businesses in India collect, use, and safeguard personal data in the digital ecosystem. Together with the Digital Personal Data Protection (DPDP) Act, 2023, these Rules create a rights-based, consent-driven framework that places citizens at the centre of data processing while still enabling responsible innovation and growth in the digital economy.

The Tata Electronics Breach: What IT & Security Teams Must Do - Before Your Business Is Next

When Tata Electronics confirmed a cybersecurity incident this week, the numbers were staggering. Over 200,000 files. 630GB of data. Apple iPhone specs. Tesla trade secrets. Employee passport scans.

The Cybersecurity Poverty Line: Why it exists and why Sophos exists to erase it

The Cybersecurity Poverty Line: Why it exists and why Sophos exists to erase it Erase is an ambitious word. We chose it because the agentic era of AI creates a genuine opportunity to change the equation. There are roughly 359 million businesses in the world. Fewer than 35,000 of them employ a CISO. Every framework, product taxonomy, analyst report, compliance regime, and piece of cybersecurity marketing in circulation assumes a senior security leader on the other end.

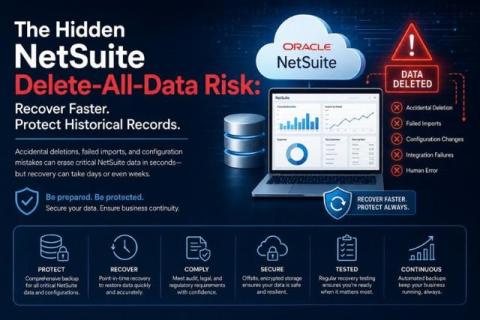
The Hidden NetSuite Delete-All-Data Risk: How to Recover Faster and Protect Historical Records

Enterprise Resource Planning (ERP) platforms have become the operational backbone of modern organizations. Finance teams rely on them for reporting and compliance, operations teams depend on them for workflows, and executives use them to make business-critical decisions. Because of this reliance, most organizations assume their ERP data is always recoverable. However, one often-overlooked risk in cloud ERP environments is the possibility of large-scale data deletion, accidental overwrites, failed imports, or configuration changes that impact historical records.

How Cuffless Blood Pressure Monitors Are Redefining Patient Privacy in Digital Health

Healthcare technology is undergoing a fundamental shift in how we monitor vital signs. Cuffless blood pressure monitors represent one of the most significant advances in this transformation-not just for their convenience, but for how they're addressing one of modern medicine's most pressing concerns: patient data privacy. As health monitoring becomes increasingly digital and continuous, the question of who controls our most intimate health information has never been more critical.

IoT Security vs Traditional Endpoint Security: What Changes?

IoT security changes the way cybersecurity teams think about assets, identity, updates, and monitoring. A laptop, server, or phone usually supports endpoint agents and user-based controls, while an IoT device often runs quietly with limited interfaces, fixed firmware, and a specific operational task.

How Modern POS Platforms Help Retailers Reduce Operational Risk

Ask a store owner to name their biggest operational risk, and you'll usually hear about the dramatic stuff. A break-in. A card-skimming scam. The walk-in cooler that quits at 2 a.m. on a holiday weekend. Those things happen, and they hurt. But they're rarely what bleeds a retail business dry.