Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

What Is AI Asset Discovery (And Why It Matters for AI Governance)

Enterprise artificial intelligence adoption is scaling at a pace that manual inventory methods simply cannot match. This rapid proliferation has created a severe visibility chasm for security and risk teams: it is fundamentally impossible to govern, secure, or quantify what you do not know exists. ‍ To bridge this gap, organizations are shifting away from point-in-time compliance audits and adopting continuous discovery.
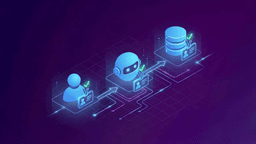
Your AI Agent Needs to Know Who You Are

When your AI agent calls an MCP tool, that tool has no idea who actually triggered the request. It sees the agent, not you. This post explains why that matters and how to fix it with Teleport JWTs. In part two of this post, we will explain how to extend this to AWS to carry your identity through Amazon Bedrock AgentCore all the way into CloudTrail.

What is compliance software?

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

The Hidden Security Risks of Unstructured Data in File Shares

Most organisations have a data problem they rarely see clearly. It is not always inside databases, CRMs, finance systems, or other structured platforms. More often, it is hidden in shared drives, old project folders, exported spreadsheets, PDFs, email attachments, archived documents, and duplicate files saved across departments. This is unstructured data. It is easy to create, easy to copy, and difficult to control. Over time, it can become one of the biggest blind spots in an organisation's cybersecurity and compliance strategy.

Leading Digital Transformation Advisory Providers in 2026

As organizations continue to adapt to rapidly evolving technologies and changing customer expectations, digital transformation remains a top strategic priority in 2026. Businesses across industries are investing in cloud computing, artificial intelligence, automation, cybersecurity, and data-driven decision-making to improve efficiency and remain competitive. However, successful transformation requires more than technology adoption alone. Organizations need experienced advisory partners that can align digital initiatives with business objectives, manage organizational change, and create sustainable growth strategies.

A Step by Step Guide to Creating Realistic Instagram Post Mockups for Presentations

A realistic Instagram post mockup can make a presentation easier to understand, especially when a campaign idea is still being reviewed. Instead of showing a loose image, a caption in a separate file, and notes in a slide, the post can be shown in a format that feels close to the final Instagram layout. This helps agencies, SMM specialists, designers, and brand teams discuss creative choices with less confusion. A good mockup is not about pretending that something was published, but about showing how a post may look before approval, portfolio use, or campaign planning.

The 3-2-1-1-0 Rule: The Gold Standard for Code Backup

SUMMARY For a long time, the classic 3-2-1 backup rule was the industry standard. It served IT professionals incredibly well. But as the threat landscape evolves, your defenses need to evolve with it. To truly protect your intellectual property and guarantee that your teams can keep working no matter what happens, your company should consider upgrading to the ransomware-ready 3-2-1-1-0 rule.

Why Abandoned Repositories Are Your Potential Data Security Gap

SUMMARY – Inactive repositories are often mistaken for harmless dead code, but they are actually open doors into your network.– Threat actors do not search manually; they use automated scanners to parse thousands of files and extract secret patterns, access keys, and credentials.– The root of this vulnerability is an organizational lack of ownership and a missing lifecycle for code that is no longer actively developed.– Discover a practical DevSecOps approach to secure your shadow

Aikido x Drydock | A way for maintainers to catch malware before it ships

Maintainers, this is for you. We're partnering with Drydock so maintainers can see exactly what's inside a package before they approve it, catching malware before it ships instead of disclosing it after. Drydock lets you read the actual bytes of a staged release before it goes live, so bad versions get caught at approval rather than in a post-mortem. For npm and PyPI maintainers, Drydock is available at no cost.

ISO 27001 Requirements: A Guide for 2026 Certification

If you're working toward certification, you're probably dealing with the same pattern many organizations encounter. Policies live in shared folders, risk decisions sit in meeting notes, control owners answer questions differently, and audit prep turns into a scramble to prove that security work happened. The hard part usually isn't understanding that ISO 27001 matters. It's translating the standard into repeatable operational evidence.