Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Every New Compliance Framework Restarts the Same Fire Drill. It Doesn't Have To.

Every compliance audit starts the same way: Someone flags a deadline, the team scrambles to pull evidence, map controls, and prove that the policies running in production actually match what the framework requires. They make it through. They exhale. Six months later, a new framework arrives, and the fire drill starts all over again. Most teams walk away from an audit believing they are compliant.

Extending the Single Source of Truth to the Agentic Software Supply Chain

Every developer on your team now runs multiple agents. None of them are waiting for human sign-off to act. That’s exactly the gap we discussed and closed at swampUP 2026. JFrog unveiled new capabilities that extend the JFrog Platform as not only the Single Source of Truth for OSS and heritage software, but now the Agentic Software Supply Chain. Here’s everything we announced, and why it matters.

Microsoft Entra ID monitoring: Detecting suspicious activity

Entra ID monitoring correlates sign-in, audit, and privileged-role activity to expose suspicious identity changes while evidence still exists. Native controls leave gaps in retention, licensing, and correlation, so resilient teams export data, baseline admin behavior, and connect to Entra ID, Privileged Identity Management (PIM), OAuth, Conditional Access, and on-premises Active Directory events in a single workflow.

AI Governance Auditing for Security and IT Teams

AI governance auditing distinguishes between a documented policy and a working control. The audit traces one AI output back through the identity that invoked it, the data it reached, the guardrail that applied, and the record retained afterward. Most programs fail because access is ineffective: nobody can say which identities access sensitive data through an AI assistant, let alone prove the limit is held.

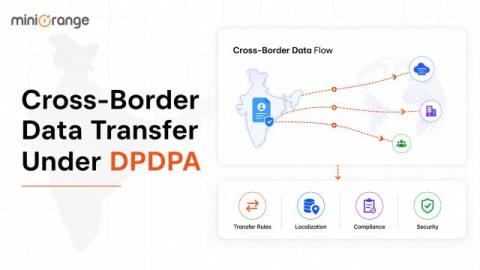
Cross-Border Data Transfer Under India's DPDPA

Businesses operating across countries routinely move personal data between India and overseas systems. Customer information may be stored by a global cloud provider, employee records may be accessed by an international headquarters, or an Indian business may use SaaS platforms whose infrastructure is located outside the country.

CISO Risk Intel Brief: Edge Zero-Days, Artifact-Repository Takeover, and Identity-Pivoted Extortion

This CISO application risk intelligence briefing covers two distinct horizons: the past seven days (Wednesday, 26 August 2026 through Wednesday, 2 September 2026) and the preceding thirty days (Sunday, 3 August 2026 through Wednesday, 2 September 2026). It is written for board risk committees and operating CISOs.

CrowdStrike Extends Endpoint Security to Stop Software Supply Chain Attacks

Software supply chain attacks pose a critical enterprise threat. In the first half of 2026, these attacks increasingly used malicious software packages uploaded to public software registries, the CrowdStrike 2026 Threat Hunting Report found. Adversaries are poisoning open-source packages and exploiting the same dependencies that AI-assisted development tools and agentic applications pull onto enterprise endpoints every day.

Design tools around information, not APIs

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

The Best Speech-to-Text APIs for Media Captioning and Broadcast Workflows

Media captioning and broadcast transcription put different pressure on speech-to-text APIs than general business use cases. Accuracy still matters, but so do low latency for live output, speaker handling, timestamp quality, multilingual support, and the ability to keep working when the audio includes overlapping speakers, background sound, remote contributors, or fast-paced unscripted dialogue.

The Screenshot Looked Better-But One AI Edit Changed the Evidence

A security analyst prepares a phishing report for publication. The original screenshot is accurate but messy: a personal email address is visible, the browser contains unrelated tabs, and a notification blocks part of the page. The analyst uses an image editor to clean it up. The result looks professional. Unfortunately, one character in the suspicious domain has also changed. Tools such as Nano Banana can edit existing images and generate new ones, but security communication introduces a requirement ordinary visual content may not have: some pixels represent facts. Improving the image cannot be allowed to rewrite them.