Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How AML Software for Accountants Can Improve Client Due Diligence

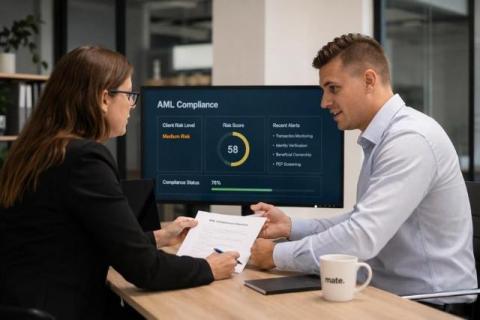
If your firm is getting ready for Tranche 2, AML software for accountants can make that process far easier. It helps you manage AML compliance, speed up due diligence, and keep client due diligence consistent from the start. Instead of relying on spreadsheets and manual follow-ups, you can use one system to check, record, and review what matters.

How to Build a More Flexible and Connected AV Setup

A boardroom gets used for a client demo on Monday, a town hall on Wednesday, and a hybrid interview on Friday. It was built for one of those. It's now handling all three, badly. That mismatch is what flexible AV design fixes. Not by cramming in more gear, but by rethinking how the room, the network, and the equipment connect to each other in the first place.

Warning: Chameleon SEO Poisoning Spreads Phishing Pages

Cloaked SEO poisoning attacks surged by 40% in the second quarter of 2026, according to researchers at Fortra. This tactic, also known as “Chameleon SEO poisoning,” uses cloaked search engine results to spread phishing sites. “Chameleon SEO poisoning,” uses cloaked search engine results to spread phishing sites.

Building the foundation for the Smart, Green Port

Ports are becoming increasingly digital. Sensors, connected equipment, private networks, IoT platforms, analytics, digital twins and AI are creating new opportunities to improve efficiency, resilience and sustainability. But adding more technology does not necessarily make a port smarter. Many ports already operate hundreds or thousands of connected assets across multiple systems, suppliers and stakeholders.

7 Best Practices for Implementing API Governance

API governance is the framework of policies, standards, and controls an organization applies to how APIs are designed, exposed, accessed, and monitored. It answers four questions for every API in your environment: who owns it, what data it touches, who can call it, and whether its behavior stays within approved limits.

Three Frameworks, Three Definitions of AI Risk

Cross-mapping tables for AI evidence in life sciences already exist and are broadly right. Data integrity practice lines up against data governance requirements, software lifecycle logs against technical documentation and logging, human review checks against human oversight duties, post-market surveillance against post-market monitoring. Build one repository, present it two ways. ‍ All of that is sound and it starts one step too late.

Single-Agent Monitoring Records Nodes, Not Edges

Monitoring an agent tells you what that agent did. Every useful question about a multi-agent deployment concerns what happened between agents, and those are properties of the connections rather than of the participants. A per-agent view records nodes and the problems live on the edges. ‍ The shortfall is not a tooling problem waiting on a product.

A Risk Number Does Not Decay on a Smooth Curve

An annual quantification gets produced in March and quoted as fact in November. Everyone involved knows the figure has aged and nobody knows by how much, so it keeps being presented with the same confidence it had on the day it was signed off. ‍ The usual framing is that a number decays gradually and needs refreshing more often. The framing is half right and it misleads on the part that matters, because most of the decay does not happen gradually at all. ‍

A Practical Guide to Attack Surface Management

Attack surface management (ASM) is the discipline of continuously discovering, inventorying, assessing, and prioritizing every asset, control, and exposure across your environment. It gives you an always-on picture of what you actually have, rather than a point-in-time scan. Done right, it answers the three questions every security leader is really asking: What do I have? Where am I exposed? What do I fix first?

Common Zero Standing Privilege Challenges and How To Solve Them

One of the most exploitable parts of modern attack surfaces is standing privileges: the persistent access rights that linger on accounts long after they’re needed. With standing privilege, static credentials are easier to steal, and overprovisioned accounts give attackers far more reach than they should have. Zero Standing Privilege (ZSP) solves these issues by granting access only when necessary and revoking it as soon as the task is finished, leaving behind no lingering access.