Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

AI SOC Adoption: Where to Start in the First 90 Days

John White is the Field CISO for EMEA at Torq. A respected security executive with more than 20 years of leadership experience, John previously served as CISO at Virgin Atlantic, where he led a multi-year transformation deploying the Torq AI SOC Platform to modernize cyber operations. Prior to Virgin Atlantic, he built and transformed security functions for global organizations, including ASOS, Liberty Global, AEG Europe, and KPMG. You’ve signed the AI SOC contract.
Every Campaign Starts From Scratch. That's the Problem

The team has launched campaigns before, yet the next one begins with the same questions. Where is the approved logo, who signs off the offer and which document contains the final headline? Experience exists, but the process seems determined to forget it every time a new deadline appears.

How Viddo Holds An Incident Diagram Still While It Moves

Security notes stay readable when the diagram does not grow a second architecture. A customer brief can start from the signed drawing on viddo, then add a short motion pass that leaves every box, arrow, and label on the same page the analyst already approved.

Turning 1-Star Reviews Into 5-Star Ratings: A Response Playbook

There are 250 million online customer reviews posted across digital platforms every day. But the volume isn't the major issue here. A single unaddressed one-star rating can instantly derail weeks of hard-earned brand momentum. Ignoring these public complaints costs real revenue when prospective buyers look elsewhere. Turning a scathing comment into a positive rating isn't about winning an argument online. It requires immediate action and strategy to transform angry customers into your most devoted brand advocates.

How To Research a Cryptocurrency Before Jumping In

A brand-new token can go from unknown to trending in a single afternoon, and that speed is a big part of crypto's appeal. It's also why jumping in blind can sting. A little homework before you buy won't guarantee a win. It can, however, help you separate promising projects from hype that fizzles out by the weekend.

How to Keep a Game Server Safe From Crashes and Data Loss

Two years of building, gone in one afternoon. It happens to a group somewhere every week. Usually it starts small. A plugin updates badly. The power blinks during a save. Someone types a command they shouldn't. And the world file ends up half-written and unreadable. None of those things are rare. But almost all of them are survivable, if you set things up before they happen. Here's how.

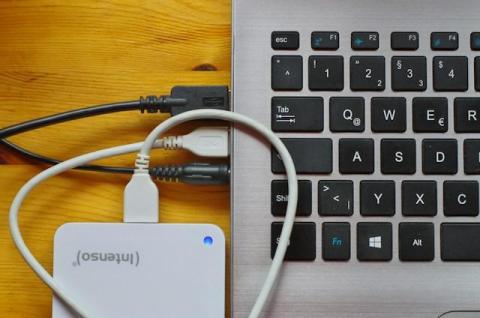
How To Review A Device Photo As Image To 3D

Hardware writeups often have one photograph and a port the photo never turned toward the lens. A reviewer can describe that port from a datasheet, or they can ask a mesh to show the hidden side so a reader can turn it. That second path is what image to 3d is for when the source is a single clear device photo, and it is a starting mesh rather than a measured scan of the board.

What Business Email Compromise Really Costs You

Business email compromise can turn one convincing message into a six-figure loss, days of disruption and a difficult recovery effort. Criminals study how an organization communicates, then impersonate executives or trusted suppliers to redirect legitimate payments. The direct financial loss may be only the beginning. Legal advice, incident response, delayed projects and damaged supplier relationships all raise the final bill. Effective protection therefore depends on coordinated email security, payment controls and verification procedures.

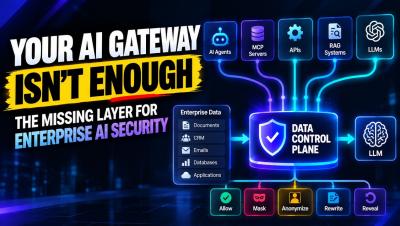
Why AI Needs a Data Control Plane (Masking and Gateways Aren't Enough)

Your AI gateway and identity platform don’t decide whether a task can use a piece of enterprise data. In agentic AI, one request can trigger multiple agents, MCP servers, APIs, RAG systems, and LLMs, and each one is a separate security decision. This video explains why enterprise AI needs a runtime data control plane. It covers why identity alone can’t make the call, why masking PII isn’t enough when business context is sensitive, and how Protecto applies allow, mask, anonymize, rewrite, or selective reveal decisions across the AI workflow. It ends with a Fortune 100 multi-agent example.

Acronis Cyber Protect Cloud is now Acronis Cyber Platform

Until October 14, 2026, services providers have known Cyber Platform as Acronis Cyber Protect Cloud, whereas corporate customers have known Cyber Platform as Acronis Cyber Protect. To simplify partner, customer and user experience, Acronis offerings for both service providers and end-customers are renamed to Acronis Cyber Platform.

CISO Risk Intel Brief: Trusted Ingress, Edge Zero-Days, and AI-Generated Code Define Residual Risk

This briefing covers material developments for the seven-day period of 14–21 October 2026 and the thirty-day period of 21 September–21 October 2026. It is written for board risk committees, peer CISOs, and security leadership. The focus is residual risk, control effectiveness, and business enablement across application security, software supply chain, cloud and infrastructure, identity, third-party exposure, and AI-assisted development.