Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

AI Agents vs. Audit Logs: What We Learned at Security Game Day

Teams of three to four, detective aliases, a magician, and a flag hidden on a Manhattan billboard. This is our second Identity Security Game Day, a tabletop CTF where Teleport engineers and customers team up to simulate the incidents that don’t happen often, but matter when they do. Game days put customers and Teleporters at the same table. You find out how people actually deploy Teleport versus how you expected, spot better ways of doing things together, and build the personal connections remote work rarely gives you.
CISO Risk Intel Brief: Record Patch Volume, Edge Zero-Days, and AI-Accelerated Supply Chain Pressure

This briefing examines material developments across the most recent seven-day period and the preceding thirty days. It is written for executive and board consumption and focuses on residual risk, control effectiveness, material exposure, and the practical implications for application security programs, software supply chain integrity, edge and identity systems, and the accelerating role of AI in both attack and defense.

Agentic Data Security: How Cyberhaven Secures Agent Workflows

Agentic workflows move sensitive data through systems that most security tools never see. This walkthrough follows one workflow from start to finish. A user shares customer data with an agent, the agent calls Model Context Protocol (MCP) servers to enrich its analysis, and the combined dataset is saved locally and shared through email, web upload, and USB. The video runs the workflow once without protection, then runs the same workflow again with Cyberhaven in place.

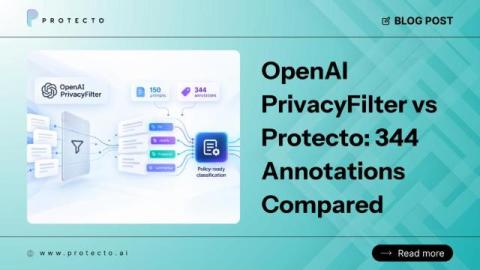
OpenAI PrivacyFilter vs Protecto: 344 Annotations Compared

Most evaluations of a PII protection layer ask one question: did it find the sensitive data? That was the right question when data loss prevention meant blocking. A DLP system that found a Social Security number stopped the email, and nothing downstream needed to understand what had been stopped. AI workflows are different. Sensitive data can enter through prompts, tool calls, retrieved RAG context, agent memory, and model outputs, including paths that may sit outside traditional DLP inspection points.

The Role of AI Calling in Secure Business Communication

Every business depends on phone conversations. Customers share account details, teams discuss deals, and managers make quick decisions over the line. Because so much sensitive information travels through voice, protecting it matters as much as protecting email or stored files. This is where AI calling has started to play a useful part. In simple terms, AI calling means using artificial intelligence to place, answer, or manage phone calls, often by understanding speech and responding in a natural way. When it is set up with care, it can make business communication safer as well as smoother.

Why AI Red Teaming Belongs at the Core of Your AI Security Program

Enterprises are putting AI applications and agents to work on sensitive data and business workflows, while attackers look for new ways to manipulate the models and exploit the tools connected to them. Security leaders need to know whether those systems will hold up against a real attack, and AI red teaming gives them that answer by testing AI the way an attacker would.

AI Trust Starts With Knowing the Source

An AI agent produces a recommendation that looks reasonable. It's accurate. The model didn't hallucinate. Can the organization trust it? That depends on questions the output can't answer: Enterprise trust requires knowing where information came from, how it moved, what happened to it, and whether the process behind the result deserves confidence. Provenance is where that trust starts.

MCP Gateway Security Controls for AI Agents

The Model Context Protocol states plainly that it cannot enforce these security principles at the protocol level, and that implementors should follow best practices in their integrations. Every control an organization gets therefore comes from where it places the gateway and what it does there. ‍ The protocol publishes its own security best practices document, currently at revision 2026-07-28, naming the attacks a deployment has to handle.

How to Monitor AI Interactions on Employee Devices

Monitoring has to happen on the device, because three categories of AI use never reach the network in a form anything can inspect. Local models run without leaving the machine. Desktop applications that pin their certificates sit on an inspection bypass list by design. A laptop on a home connection routes through nothing the organization operates at all. ‍ The uncomfortable part is that the first two are deliberate. Somebody approved the bypass, and the approval was correct on its own terms. ‍

Agents Are Acting. Most Organizations Cannot Stop Them.

Nearly half of the organizations we surveyed — 49.8% — confirmed or suspected that an AI agent in their environment took an action in the past year that nobody intended, expected, or authorized. That is not a prediction. It is what security and technology professionals told us when we asked them directly, across a survey of over 380 organizations, about their experience over the last 12 months. Agentic AI has moved fast. The data shows it has moved faster than most organizations can govern.