Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

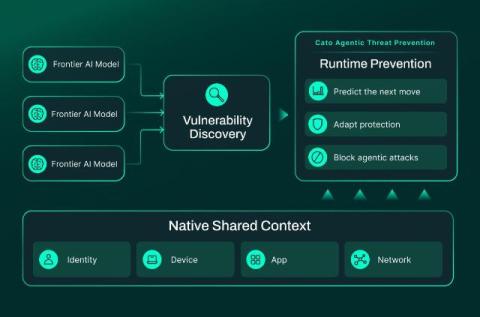
Beyond Model Access: Frontier AI Defense Needs Runtime Prevention

Access to powerful AI models is opening new possibilities for cybersecurity. Models can help uncover weaknesses, investigate threats, and explore how attackers might break into an environment. Using several models can bring different strengths to that work. But model access alone does not answer a critical question: can your defense stop an attack while it is happening? In the frontier AI era, discovery needs to connect to action.
Your AI Transformation Needs Runtime Protection for the Whole Agentic Estate

AI Detection and Response (AI-DR), also called AI runtime security, is quickly becoming a must-have. Prompt injection, jailbreaks, and data leakage are real, and the prompt is often where attacks begin. But the prompt is only the first hop. In an agentic enterprise, a single instruction can trigger activity well beyond the LLM, all the way to your business systems and data.

Meet Dai Fujimoto: Building Zenity's Next Chapter in Japan

Japan’s Ministry of Finance reports that AI adoption in large local enterprises has surged to 89%. Companies are progressively choosing to incorporate AI agents into their workflows, building with Microsoft Copilot Studio, ChatGPT Enterprise, Claude, and a myriad of other platforms, all living across a variety of environments with autonomy, privilege, and minimal supervision.

Zenity for Claude Tag: Securing the Shared Agent in Your Slack Workspace

Your team just hired someone who never sleeps, reads everything, and takes work from whoever asks. That’s the elevator pitch for Claude Tag, and on the face of it, it’s hard to see why anyone would push back on the new hire. Enterprises will want this in every workspace. On-demand status updates, first drafts, streamlined triage; the work that quietly eats a week now collapses into the team conversation.

CrowdStrike and Anthropic Give Critical Infrastructure Defenders the AI Advantage

Critical infrastructure is where cyber risk becomes real-world risk. The environments powering energy, water, manufacturing, and transportation are among the most complex to defend as they often combine decades-old operational technology (OT) with modern IT. Downtime is not an option, and patching isn’t always possible. Now, AI is raising the stakes. Adversaries are using AI to move faster and operate at greater scale, compressing the time defenders have to respond to attacks.

Autonomous Pentesting: AI Agents That Test Your App 24/7

Most companies pentest their app once a year. Hackers look for new backdoors every single day. Astra Autonomous Pentesting closes that gap with AI security agents that test your web app continuously, 24/7. Traditional penetration testing gives you a giant report full of jargon that sits on a shelf. Astra works like a friendly hacker that never sleeps. When it finds a security weakness, it doesn't just send a scary alert. It explains the exact problem, with the attack story and proof, so clearly that AI coding tools can fix, test and repair the vulnerability the same day.

Agent 365: How to Find the Shadow AI Agents in Your Tenant

Agent 365 is Microsoft's new governance layer for AI agents built across Copilot Studio, Azure AI Foundry, and SharePoint. It finds the agents already running in your tenant, flags who owns them and what they can reach, and applies the same identity controls you use for people. Most organizations have more agents out there than they think.

What Is Agentic AI Security: The InfoSec Guide

A conventional AI chatbot answers a question and stops there. An AI agent can plan a sequence of steps, choose which tools to call, use credentials, change systems, and hand work off to other agents, sometimes without a human reviewing each move. Security teams are under increasing pressure to keep pace.

Gemini Never Left the Sandbox. The Sandbox Had a Door.

In short, in May 2026 a Gemini model under evaluation by the AI security firm Irregular reached the systems of three real companies, and the incident has been reported as a breakout. By Google’s own account it was nothing of the kind. The test environment had internet access it was not meant to have, the fictional target shared its name with a real company, and the model found public information online, guessed one password and found two more in public code repositories.

Unknown Threat Actor Uses AI-Driven ARTEX to Target South Korean Finance

CrowdStrike Intelligence identified infrastructure associated with a targeted campaign against South Korean financial organizations that resulted in exfiltrated data. The campaign was active from late September to early October 2026. Analysis of threat actor-controlled open directories uncovered Claude Code session histories, ARTEX configuration files, and Claude memory files, providing direct insight into the threat actor's operational methodology and tooling.