Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Prompt Injection as the Defense Against Autonomous Cyberattacks?

I’ve watched AI-powered cyberattacks inch closer to autonomy throughout 2026, and I can point to dozens of real-world incidents as proof. AI-enabled cyberattacks surged by 56% over the last year, meaning 1 in 4 (25%) malicious breaches now involve artificial intelligence. The important one: on May 10, 2026, researchers documented the first fully autonomous LLM-driven post-exploitation attack in the wild.

Sophos AI Defense is now generally available

Bring AI out of the shadows with visibility and control that help your organization adopt AI securely. When we introduced Sophos AI Defense in July, we focused on a challenge facing organizations everywhere: AI adoption is accelerating, often faster than security and IT teams can see or control it. New AI tools, embedded capabilities, and shadow AI are creating blind spots around where AI is being used and what information it can access.

AI governance needs more than a policy document

AI tools have made it remarkably easy for a company to expose its own data: None of these actions seem malicious, but each one moves sensitive information somewhere the security team cannot see. This new era of "move fast and break things”, a phrase famously coined by Mark Zuckerberg in the early Facebook days, benefits attackers. Company data now flows through more places, more third parties, and more delegated credentials.

The Quiet Takeover: How Your Forgotten Cloud Resources End Up Selling Slot Machines

Picture a global telecom company. Three years ago, a marketing team launched a campaign microsite on a cloud platform and pointed a company hostname at it. The campaign ended and the team deleted the app. Nobody deleted the DNS record. A few years ago, that mistake could sit there for a decade. No one was looking. Today, attackers run automated sweeps across millions of domains, resolving every DNS record and checking whether the resource behind it still exists.

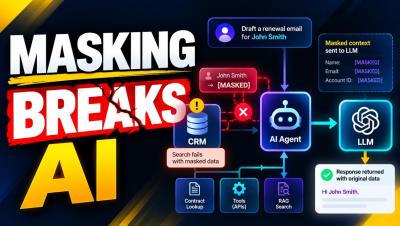
Why Data Masking Breaks AI Workflows (And What Works Instead)

What if masking sensitive data actually broke your AI application? Most AI security strategies start with a simple rule: mask sensitive information before it reaches the LLM. But real AI workflows are more complex. An AI agent might need to search a CRM, retrieve a contract, check account details, call external tools, and generate a response. Each step may require a different level of access to sensitive data.

Agentic AI and PCI DSS: What Happens When AI Agents Reach Checkout?

An AI shopping assistant can recommend a product without being allowed to buy it. An agentic AI system may go further: access an account, select a payment method, interact with a checkout, and initiate a transaction. Each added permission changes the payment-security questions you need to answer. Before adding an agent to a payment journey, draw its boundary. What can it read? What can it change? What can it authorize? What happens when it encounters content controlled by someone else?

Introducing Sophos AI Defense

Sophos AI Defense finds the AI tools employees and applications are using, including the ones security teams never approved, and enforces policy wherever they run. Every AI tool an organization can’t see is a potential gap in confidentiality, integrity, and availability. Delivered through Sophos Fusion, the AI-native cybersecurity defense system, Sophos AI Defense connects controls on the device, across the network, at sign-in, and in the browser into one line of defense, so teams can safely adopt AI faster without adding another disconnected tool to manage.