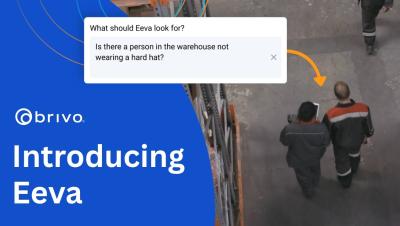
Meet Eeva—the AI video agent inside the Brivo Eagle Eye VMS (Video Management System) that transforms how you manage, monitor, and interact with your business's security cameras. Instead of just recording footage, Eeva actively watches for the specific events that impact your business daily. No AI training or coding required—just type what you want Eeva to look for in your own words. What can Eeva keep an eye on for you?
For years, companies treated shadow IT primarily as a policy and control problem. Employees have always found and used technology outside the approved IT stack, from unauthorized endpoint applications and browser extensions to personal cloud services. It left a trail: an install, a device on the network, something a scan or an agent could eventually catch. From there, an analyst had to investigate the finding and assess the risk before deciding how to respond.
The agentic AI security conversation has, for good reason, spent most of its energy on the agents an organization builds or deploys directly: what they're authorized to do, what data they can reach, how their behavior is monitored. I think that focus is necessary and also increasingly incomplete, because the fastest-growing risk surface in agentic AI right now isn't the agents themselves.
Most GRC platforms claim to use AI. That makes it harder, not easier, to judge the near-identical claims in every demo. Leaders need to know the standards to hold these claims to, what can actually be verified, and how to tell two product pitches apart before letting one of them touch critical controls. It helps to split what you are looking at into two groups: demo-grade AI and enterprise-grade AI. Nearly every GRC vendor now describes itself as the second.
A phishing campaign is using AI-themed lures to target employees who operate advertising accounts, according to a new report from Island. The campaign is launched from a phishing platform that poses as a portfolio of AI advertising tools, using branding from Gemini, Claude, ChatGPT, Perplexity, and Muse. The platform’s operator added a fake Muse Ads lure eight days after Meta launched its Muse AI agent.
An audit trail is usually judged by how much it contains. The more useful question is how many innocent explanations it rules out, because a record that admits a benign reading supports an assertion rather than a conclusion. Each source added to a trail removes an alternative explanation rather than adding detail. Confidence therefore climbs in steps rather than smoothly, and three sources of the same kind are worth less than two of different kinds.
Enterprise AI governance guidance assumes a review board that meets monthly, an independent validation function, an impact assessment per system and somebody whose job title contains the words AI and compliance. A company of three hundred people has none of those and is governed by the same regulations. The difference runs deeper than budget. Enterprise programs are assessment-led, which scales with headcount because every system needs an assessor.
Reach brings autonomous defense to the security controls organizations already own. AI-powered attackers can find and exploit misconfigured controls, configuration drift, and unpatched vulnerabilities in minutes. Reach helps defenders find and close those gaps first. It mitigates vulnerabilities with compensating controls, autonomously finds and fixes misconfigured security controls, and stops configuration drift.