Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Govern the AI agent as the identity it is

AI agents are non-human identities. They hold credentials, carry permissions, and act on systems around the clock, usually with standing access nobody reviews. The Salesloft Drift breach reached more than 700 organizations through exactly that kind of over-scoped, non-expiring token, with no prompt injection involved. The controls already exist: inventory every agent, scope it to least privilege, expire its access, review it on a schedule, and detect when it's abused.
Build the Self-Driving SOC with Tanium Security Operations

Attackers don't wait for humans, and neither should your SOC. Tanium Security Operations brings detection, investigation, hunting, and response together on one platform that moves at machine speed. See how Tanium Atlas works as an extension of your team: pulling live telemetry, historical activity, and the full process tree the moment a threat surfaces, hunting a hypothesis across every endpoint in your fleet, and containing threats from one endpoint to hundreds of thousands. When the hunt needs to go deeper, HuntIQ's hands-on experts take it from there, inside your environment.

Governing at the speed of AI: What IT leaders need to know

AI is reshaping the IT leadership role faster than any shift in the last decade. As AI makes it dramatically easier to build software (agents, apps, automations, and more), the volume of software entering the enterprise is far beyond what IT teams have had to govern before. That shift demands new ways of thinking about enterprise control: how security, access, and oversight evolve to keep pace with software that's built faster and by far more people than ever before. The leaders who treat this as an operating shift, not just a technical one, are the ones expanding their influence.

Securing Your AI Agents: Native AI Detection and Response Across the Full Agentic Path

Enterprises are deploying AI agents at scale, and those agents are taking real business actions. Through LLMs, MCP servers, and APIs, they move money, access patient records, modify code, and send emails. The attack surface has fundamentally shifted, but most security programs are still focused on what an AI says rather than what it does.

AI Governance Where the Regulator Also Runs the Market

AI governance evidence is usually prepared for a neutral reader. A regulator with no stake in the market, an auditor with no competing product, an examiner who gains nothing from what the documentation contains. ‍ In securities and derivatives markets that assumption does not hold. Exchanges and clearing organizations register as self-regulatory organizations, and most of them operate the market while regulating its participants. The reader of your evidence is also an operator. ‍

Request, Aggregate, Bypass: How Attackers Can Evade LLM Safety Classifiers

Modern frontier AI models deploy safety classifiers. These are second AI models that sit between the user and the frontier model, evaluating every request in real time. If a request is flagged as harmful, the classifier blocks it before the model can respond. Significant investment and safety model expertise have made these classifiers effective. Anticipating how adversaries circumvent these systems is a security problem that requires different expertise.

Zero Trust for AI Agents: Enforcing Anthropic's Framework

AI has changed how work gets done. Agents can plan tasks, query enterprise repositories, invoke tools, write code, call application programming interfaces (APIs), and take actions across connected systems. As they work, they create, copy, fragment, transform, and share data across workflows. A perimeter and a one-time authorization decision do not provide enough control for this operating model. An agent can chain permissions, tools, integrations, and data sources while completing a task.

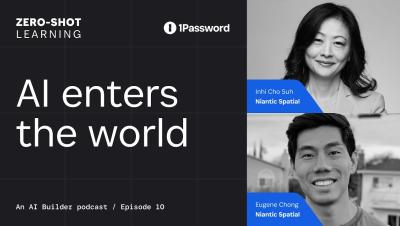
AI enters the world with Inhi Cho Suh from Niantic Spatial | Zero-Shot Learning

Despite the wealth of information LLMs draw on, they are not reliably grounded in the physical world. Spatial knowledge is rarely written into agentic development and remains invisible to LLMs. This episode’s guests, Niantic Spatial’s CEO Inhi Cho Suh and Director of Product Management Eugene Chong, are building a grounding layer to fill that gap. Inhi and Eugene join 1Password CTO Nancy Wang and Google Gemini’s Dev Tagare to discuss why spatial understanding is a prerequisite for AI systems operating in the physical world and the grounding layer for world models to make spatial data precise and useful to AI.