Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How a Hacker Used Standard AI to Dismantle a Government

The real shock is not a restricted model with scary branding, it is what standard public AI tools already make possible. A prolonged attack against government systems, tax records and voter data shows the threat comes from scale and persistence, not only from the newest frontier release.
Continuous Threat Exposure Management (CTEM): The Complete Guide to Proactive Cybersecurity

The cybersecurity landscape has fundamentally changed. Organizations today manage sprawling digital environments - cloud workloads, remote endpoints, SaaS applications, third-party APIs, and hybrid infrastructure - all of which expand the attack surface at a pace that traditional security programs simply cannot match.

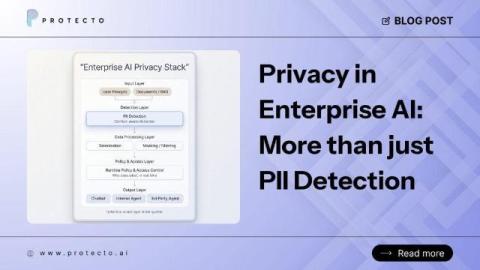
Privacy in Enterprise AI: Why It's the Foundation, Not a Feature

Last week, OpenAI released Privacy Filter, an open-weight model for detecting and redacting PII in text. It is a thoughtful release: Apache 2.0 licensed, able to run locally, designed for high-throughput workflows, and built to go beyond regex-based detection. This is good news for everyone building enterprise AI. Privacy at the model layer is getting real attention. What we liked most was how clearly OpenAI described the role of the model.

How Do AI Agents Create Data Exfiltration Risk?

AI agents create data exfiltration risk by combining three capabilities that are dangerous together: access to private data, exposure to untrusted content, and the ability to communicate externally. When all three exist in one agent, an attacker can hide instructions inside an email, document, or webpage the agent processes and trick it into sending sensitive data out. No software vulnerability is required. The attacker doesn't need to break in. They just need to talk to your agent.

Agentic SecOps: Build a security AI agent that automatically investigates detections

A credential access event fired. An AI agent investigated it, correlated it against running processes, assessed the risk, and closed the ticket. No analyst touched it. The entire loop ran in minutes. This is what security operations look like when AI can actually operate in the environment rather than advise from outside it. Security operations have always required a special kind of person.

The Configuration Drift Behind the Teams Helpdesk Breach

On April 22, 2026, Google's Threat Intelligence Group and Mandiant disclosed a campaign by a threat actor they're tracking as UNC6692. The group breached enterprise networks by impersonating IT helpdesk staff over Microsoft Teams, ultimately exfiltrating Active Directory databases and achieving full domain compromise. What's notable about UNC6692 is what they didn't do. They didn't use a zero-day. They didn't exploit a software vulnerability.

Measuring Real Risk Reduction Across Your Security Stack

Garrett Hamilton recently presented at the North Texas ISSA Lunch & Learn in Plano, TX to talk about what risk reduction actually looks like in practice. Reach shows customers exactly which controls they've deployed, the user impact of those changes, and how much risk has been reduced across IAM, EDR, email, firewall, and SASE. Not feature checklists. Targeted, measurable outcomes tied to the business.

Exposure Prioritization Agent: Demo Drill Down

Vulnerability volume continues to rise, making it difficult for security teams to determine which exposures actually matter. Without clear prioritization, teams are forced to react to volume, often focusing on severity scores instead of real risk. In this demo drill down, we showcase the Exposure Prioritization Agent within Falcon Exposure Management. You’ll see how AI-driven prioritization uses ExPRT.AI, adversary intelligence, and business context to reduce millions of vulnerabilities into a focused set of high-risk exposures.