Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

PDPA Compliance for Digital Products: What Singapore Businesses Need to Know in 2026

Singapore's digital economy continues to grow rapidly in 2026. Businesses are launching SaaS platforms, eCommerce websites, fintech portals, customer dashboards, and mobile applications faster than ever. At the same time, consumers are becoming more aware of how their personal data is collected, stored, and used. This shift has made compliance with Singapore's Personal Data Protection Act (PDPA) a critical requirement for every digital product.
How Bank Statement Analyzer AI Tools Are Simplifying Financial Management

Managing personal finances has become significantly more complicated over the last decade. Most people no longer rely on a single bank account or one payment method. Daily transactions are spread across debit cards, credit cards, subscriptions, online banking platforms, digital wallets, and international payment systems. As financial activity becomes more fragmented, understanding spending habits manually becomes increasingly difficult.

Frontier AI and the Demise of Hardware Security

The cybersecurity industry has long relied on a simple idea: find vulnerabilities, patch them, and measure success by how fast you close the gap. “Time-to-patch” became a badge of honor. That model no longer holds. The rise of Mythos-class Frontier AI Models introduces a different kind of threat. AI-driven, agentic attacks operate continuously, discover weaknesses automatically, and execute at a scale no human team can match.

Falcon AIDR Detects Threats at the Prompt Layer in Kubernetes AI Applications

AI is introducing a new class of threats that don’t look like traditional attacks and can’t be detected with conventional tools. The AI applications that organizations deploy in the cloud interact with large language models (LLMs) through prompts and responses. This prompt layer has emerged as a new attack surface, where risks like prompt injection and sensitive data leakage can go unnoticed.

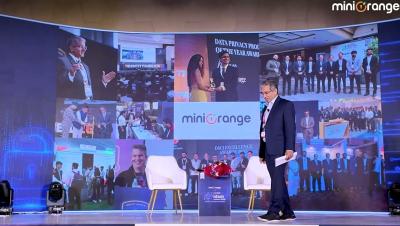
Session on How much of Mythos based attacks can you prevent using modern IDAM techniques?

In this session at ETCISO IDAM Summit 2026, our Founder & CEO Mr. Anirban Mukherji discussed Identity Access Management (IAM), data protection challenges, and AI governance for modern organizations. He covers SSO, MFA, legacy system hurdles, DBT data flows, Shadow AI risks, and practical steps like patch automation, least privilege access, and AI agent controls. Drawing from the Abhimanyu Chakravyuh metaphor, he explains how strong IAM contains breaches. Learn about vendor sovereignty, geopolitical risks, and miniOrange's expertise in IAM, AI security, and privacy.

DevOps Threats 2026: GitProtect Reveals AI and Compliance Danger Zones

As DevOps environments become primary attack surfaces, protecting your intellectual property (IP) requires a data-driven understanding of the modern threat landscape. The 2026 “DevOps Threats Unwrapped Report” by GitProtect accelerates building your cyber awareness. It brings you the latest statistics, highlighting contemporary trends in DevSecOps. It also dives into dozens of real attacks and breaches affecting SaaS platforms in 2025 in 10 different areas.

EU AI Act Compliance Checklist - A Practical Guide for Businesses

An EU AI Act compliance checklist is a structured framework that helps organisations systematically identify, classify, and govern all AI systems within scope of Regulation (EU) 2024/1689. It covers AI system inventory, risk classification (unacceptable, high-risk, limited, and minimal), conformity assessment requirements, technical documentation (Annex IV), human oversight obligations, GPAI model obligations, and post-market monitoring.

Navigating the Cybersecurity Landscape in India Empowering Human and AI Agents

The Asia-Pacific and Japan (APJ) region, with its dynamic economic growth and technological advancements, presents unique challenges and opportunities in the realm of human risk management and agentic risk management, particularly within the financial services sector. As financial institutions strive to protect themselves from increasing cyber threats, they must align their security practices with the regulations set forth by central banks across the countries.

The Rise of Cyber Threats and AI in the Philippines: A New Era Beyond Legacy Security

The Philippines, like many other nations, is witnessing a dramatic increase in cyber threats, fueled by the rapid adoption of digital technologies and the proliferation of sophisticated cybercriminals. This article examines the evolution of cyber threats in the Philippines, with a focus on phishing, email security and the risks posed by agentic AI.

Six MCP Security Incidents Every Security Leader Should Know

In July 2025, an AI agent reviewed a support ticket, queried a production database, and leaked integration tokens directly to the attacker watching the thread. Months earlier, another AI followed "hidden instructions" in a public repository, exfiltrating private code into a visible pull request. In both cases, the AI wasn't broken; it simply obeyed the attacker instead of the developer.