Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Sophos Launches CISO Advantage, Bringing CISO-Level Security Strategy Within Reach of Every Organization

Delivered through Sophos Fusion, Sophos CISO Advantage uses agentic AI with human judgement to give every organization, with or without a CISO, a security program it can measure, fund, and prove.
From audit season to always-on: what continuous network compliance looks like

Every network compliance calendar follows the same pattern: quiet between audits, then a spike of scrambling the week before the next one is due. During the quiet stretch, nobody actually knows whether firewall rules, segmentation, and access policies still hold as configured across the network. The audit does not create compliance. It samples it once, and then everyone moves on until the next one comes due.

IAM Cost Optimization: How to Reduce Identity Management Spend Without Sacrificing Security

According to Gartner survey data, 56% of CISOs increased their IAM budgets in 2026 compared to 2025 to curb evolving threats, support AI adoption, and manage complex digital ecosystems. The question is: can IAM cost be optimized without reducing security quality? There are instances where organizations keep paying for overlapping tools, manual provisioning workflows, and help desk tickets that a properly automated platform would eliminate outright.

How to Build a Data Security Program for Generative AI

Ask five security leaders what "data security for generative AI" covers and you'll get five different answers. Some may point to an existing DLP rule for ChatGPT, while others would point to an AI acceptable use policy. Some operate under the assumption that their DSPM vendor already handles genAI security. The confusion isn't about effort, as most teams are actively trying to get ahead of GenAI risk.

How to Remain Audit-Ready with Egnyte

Compliance regulations like CMMC, FINRA, and SEC don't pause, and neither should your audit readiness. Egnyte's Regulation-to-Audit framework is an end-to-end compliance solution that maps regulatory requirements directly to controls, artifacts, and audit-preparedness — keeping your organization compliant 24/7/365. Four powerful capabilities power this continuous compliance loop: · Sensitive Content Protection: Automatically scans, classifies, and labels regulated content across Egnyte and your connected repositories.

Sophos CISO Advantage is now generally available

Take control of your security outcomes. Sophos CISO Advantage is now generally available to the market, giving CISOs and security teams without a CISO the solution they need to build, manage, and improve a compliance-driven cybersecurity program. In July, we introduced Sophos CISO Advantage, explaining how it enables organizations and Managed Service Providers (MSPs) to understand cyber risk, prioritize what matters most, and demonstrate measurable improvement over time.

What Is AI Governance? A Practical Framework for Security Teams

The speed of AI integration is rapidly outpacing corporate governance capabilities. Generative AI is now embedded in development workflows and business applications, while agentic AI can make decisions and take actions with limited human intervention. That governance gap is becoming harder to ignore. Gartner predicts that more than 40% of agentic AI projects will be canceled by the end of 2027 because of escalating costs, unclear business value, or inadequate risk controls.

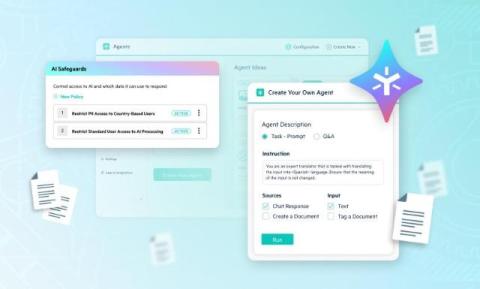
In AI Pilot Mode? Learn How to Scale AI Securely Without Shadow IT

You’ve seen the demos. You’ve run the pilots. Maybe you even deployed something that works, but is it scaling? Are your users utilizing it on a daily basis, or as intended? Or is it quietly gathering dust next to the last three tools that were supposed to change everything? Scaling AI the way most vendors describe it—connecting more tools and piping more data into more systems—doesn’t lead to progress or productivity. Rather, it results in additional risk.

CrowdStrike Expands Federal SOC Modernization Through CISA-Funded SIEMaaS

CISA has called SIEM-as-a-service (SIEMaaS) “the Rosetta Stone” for visibility for good reason. Federal defenders need to see what is happening across increasingly complex environments, understand what matters, and turn that context into action before an adversary achieves its objective.