Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How APRA's AI guidance impacts banks and insurers in Australia

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.
Keeper Security and SailPoint Partner to Automate Privileged Access Governance

Keeper Security, the leading zero-trust and zero-knowledge identity security and Privileged Access Management (PAM) platform, today announces an integration with SailPoint, a leader in identity governance, access and compliance. The Keeper SaaS Connector links SailPoint’s IGA platform directly to KeeperPAM. The integration allows SailPoint to control the provisioning, deprovisioning and entitlements of Keeper users, vaults and managed resources.

How we deployed post-quantum TLS without any code changes

In March, we announced our first major post-quantum milestone. Customers using a compatible browser could negotiate X25519MLKEM768 when connecting to the 1Password web app. This protected browser traffic from harvest-now, decrypt-later attacks (HNDL) without any customer action required. While this release raised the bar, it did not cover other ways customers connect to 1Password.

Your First Dark Web Scan Report, Explained

Most people don't hesitate to run a free security scan because they doubt it'll find anything. They hesitate because they don't know what the results will look like. Will it be 40 pages of raw data without context? A sales pitch disguised as a report? We'll walk through it screen by screen so you know exactly what to expect before entering a domain.

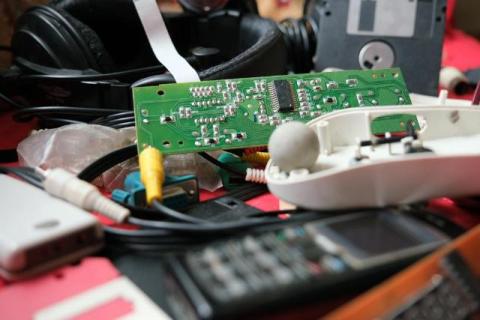
Why Retired IT Equipment Can Become a Cybersecurity Blind Spot

The security team at a mid-sized insurer spent eighteen months hardening everything that faced the internet. They rotated credentials, tightened their identity provider, and ran tabletop exercises until the incident playbook felt routine. Then a contractor bought a pallet of decommissioned laptops at a regional auction and found four of them still booting into a cached domain profile. Nothing had been breached. The data simply walked out through the loading dock, on equipment the company had already stopped thinking about.

Protecting Assets from Cyber-Physical Attacks

Our digital and physical worlds are now closely linked. This connection brings incredible efficiency, but it also creates new vulnerabilities. When digital systems control physical infrastructure, a security failure can have real, tangible consequences. Protecting your assets today means having a strategy that tackles threats in both these areas at the same time.

AI governance monitoring: how to prove your program is actually working

Ask a governance lead which of their AI controls actually ran last Tuesday at 2:14 p.m., when a specific agent touched a specific dataset, and the answer usually arrives as a policy document, an org chart, and a shrug. That gap between the controls a program claims to have and the controls that actually fired when an agent acted is where AI governance quietly fails. Policy documents describe intent. Model monitoring tracks accuracy and drift.

Two Reporting Clocks on One AI Product, Only One Running

An AI product sold in Europe is described as facing two incident reporting duties. One under product security rules and one under AI rules, with different triggers and different deadlines. ‍ Only one of them is running. Article 14 of the Cyber Resilience Act has applied since 11 September 2026. The AI duty moved, and coverage published in the last few weeks still describes it as live. ‍