Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

DMARC Explained: How to Stop Attackers From Impersonating Your Domain

Email is still the most common way attacks begin. Phishing, business email compromise, and brand impersonation all rely on one simple weakness: by default, anyone can send an email that claims to come from your domain. The protocol that email runs on was never built to verify who a sender really is, so a criminal can forge the "From" address to look exactly like it came from your company, and the receiving mail server has no built-in way to know the difference. That is the gap attackers exploit, and it is the gap DMARC was designed to close.
Global Bitcoin ASIC Miner Benchmark 2026: Comparing Efficiency and Rack Density Across Leading Models

In 2026, Bitcoin mining hardware is no longer judged by nameplate hashrate alone. As hashprice compresses and network difficulty rises, Bitcoin ASIC efficiency increasingly determines how long a machine can remain above its shutdown price. Yet J/TH is only the starting point. The power efficiency ratio shapes miner-side electricity demand, while mining rack density determines how much usable hashrate a facility can extract from limited power, cooling capacity and rack space.

RTO vs RPO: What They Mean and How to Set Them Honestly

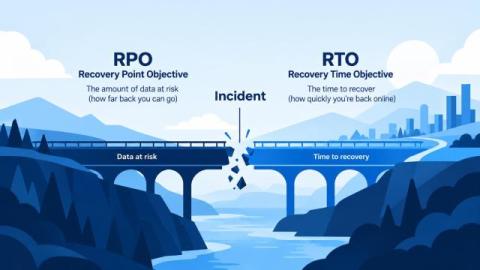
Recovery time objective (RTO) is how long a system can be down before the impact becomes unacceptable. Recovery point objective (RPO) is how much data the business can afford to lose, measured as a window of time before the incident. RTO looks forward from the moment things break. RPO looks backward from it. That distinction takes a paragraph to explain and years to get right, because the difficult part was never the definition.

Millions of Phishing Emails Use ASCII Smuggling to Bypass Security Filters

A massive phishing campaign is using invisible Unicode tag characters to evade security filters, according to researchers at Microsoft. This technique, known as “ASCII smuggling,” has grown popular over the past year for launching AI prompt injection attacks, but the same tactic can hide suspicious text in emails.

The New Agent Control Standard Names the Controls, Not Their Value

The OWASP GenAI Security Project unveiled an Agent Control Standard in early September, donated to the project and aimed at runtime enforcement for agentic systems. It sets out that agents should be inspectable, traceable and instrumentable, with declarative hooks and policy enforcement across frameworks. ‍ It answers which controls belong around an agent.

Why AI Review Cannot Keep Up With the Decision

That human review becomes a bottleneck as agents scale is now widely observed. Five or ten agents working in parallel produce more decisions than one reviewer can evaluate, and under queue pressure the review degrades into approval without examination. ‍ The usual response is to move up a level, reviewing intents and boundaries rather than individual outputs.

Autonomous Pentesting Is About To Kill Security Abbreviations

I have watched the security industry run a very profitable game with abbreviations for the last decade. The simple way to do it is to invent a category, give it a cool catchy abbreviation, market it as the missing piece of the stack, and repeat. The greatest examples are CTEM, BAS, ASM, and EASM. Every one of them arrived promising to close the gap the last one left open, and every one of them ended up as a line item on a renewal spreadsheet that nobody at the buyer‘s side could confidently defend.

Can Autonomous Pentesting Rescue CVE Coverage From Vanity Metric Hell?

The security industry killed CVE coverage as a credible metric, and it deserved to die. Vendors inflated the numbers for years in the name of depth, and nobody in the room had an incentive to ask whether they reflected real validated risk or just a longer signature list. So “CVE coverage is a vanity metric” became earned consensus. The question I keep coming back to is whether the autonomous pentesting era makes that consensus outdated.