Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

AI Security Has a Context Problem

The problem is not a lack of controls. It is connecting them into one attack story. The more time I spend with enterprise AI deployments, the clearer one thing becomes: AI security is incredibly fragmented. There are LLM guardrails, AI gateways, MCP security tools, API security, endpoint controls, SASE, code scanning, and runtime detection. Each solves a real problem, but agentic systems do not experience them as separate layers, and neither do attackers.
Identity Risk: 5 Access Pathways Emerging Across Threat Intelligence

It’s not a secret that phishing, stolen credentials, and human error remain some of the easiest ways for attackers to get into an environment. Identity has become one of the biggest attack surfaces for organizations today because sometimes, all an attacker needs to do is log in. That access can come from valid credentials, stolen sessions, exposed tokens, compromised service accounts, or abused application permissions.

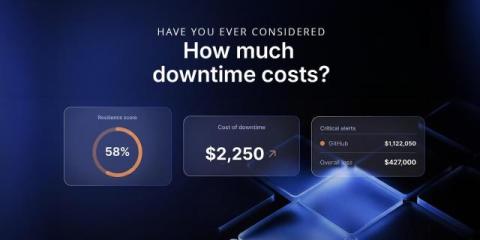
Have you ever considered how much downtime costs?

9,255 hours and 26 minutes. That’s the combined downtime and degraded service duration that GitHub, GitLab, Bitbucket, Azure DevOps, and Jira publicly reported in 2025, across 607 incidents tracked in our DevOps Threats Unwrapped 2026 report. Critical and major incidents rose 69% year over year, with overall incident volume growth at 40%—a trend that cannot be ignored and a related cost that must be properly measured.

How to Protect Backups from Ransomware

Ransomware crews go after backups first. Before any production file gets encrypted, they hunt down your backup catalog, snapshots, and repository credentials. The real question is whether your backups can survive an attacker who is actively trying to destroy them. This guide covers how to protect backups from ransomware with specifics: immutable and WORM storage, the 3-2-1-1-0 rule, air-gapping, network segmentation, encryption, and access controls that hold up under pressure.

So I asked my agent instead...

Evo already knows which AI Assets your teams pulled into your repos, which MCP servers and skills are sitting on your developer machines, which of them carry risk, and which policies they break. Getting to any of it created friction: you leave the tool you are working in, filter a UI, export a CSV, and rebuild the chart you built last quarter, every time it’s needed.

Emerging Threat: (CVE-2026-69197) Umbraco CMS Protected Content Disclosure via Delivery API Expansion

CVE-2026-69197 is an authorization flaw in the Content Delivery API of Umbraco CMS, an open source ASP.NET content management system. The Delivery API enforces member and Public Access checks on the node a caller directly requests, but it does not apply those same checks to nodes referenced through Content Picker or Multi-Node Tree Picker properties. The gap extends to pickers nested inside Block List, Block Grid, and Rich Text Editor blocks.

What It Takes to Say an AI Control Reduces Loss by a Number

Saying a control reduces exposure is easy and almost always true. Saying it reduces exposure by a specific amount is a different claim, and the machinery for producing one is well established. Set a baseline from frequency and magnitude ranges, simulate, re-estimate the ranges with the control in place, simulate again, and report the difference. ‍ The method is sound. Applied to AI controls it runs into two problems, one about which term the control touches and one about what the estimate rests on.