Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

From Agreement to Action: What's Actually Stopping Us?

Over the course of this series, I’ve laid out the case for a fundamentally different security operating model — one built around Outcome, Judgment, and Execution layers, where AI handles the execution at machine speed, and humans focus on the decisions that actually need them. I’ve argued that the CISO’s role is changing, that human-centric security no longer scales, and that the org chart needs to reflect where AI fits on the team.

The Howler Podcast: Three Year Anniversary

The Howler Podcast is 3! Join Chelsea and Mary as they reflect on the past three years and chat with special guest, Brian NeSmith, Co-founder & Executive Chairman! Interested in running with the pack? Explore careers at Arctic Wolf—one of the fastest-growing and exciting cybersecurity companies in the world, to learn about how you can join our Pack, create impact, and influence what’s next in security operations.

How CISOs Should Brief the Board on AI in the SOC

John White is the Field CISO for EMEA at Torq. A respected security executive with more than 20 years of leadership experience, John previously served as CISO at Virgin Atlantic, where he led a multi-year transformation deploying the Torq AI SOC Platform to modernize cyber operations. Prior to that, he built and transformed security functions for global organizations, including ASOS, Liberty Global, AEG Europe, and KPMG.
Featured Post

Increasingly Dangerous Threats, Not More Alerts, Are the New SOC Challenge

For years, security operations centres have operated under the same constraints of more alerts than analysts, more investigations than hours in the day, and more pressure than most teams can sustainably absorb. That imbalance is becoming dangerous as frontier models rapidly improve at finding vulnerabilities and turning them into exploits, while defenders are left dealing with the consequences in real time.

CrowdStrike Delivers the Next Evolution of the Agentic SOC

The average adversary breakout time is now 29 minutes, with the fastest recorded at 27 seconds, according to the CrowdStrike 2026 Global Threat Report. AI is supercharging the adversary playbook, empowering many to move faster across multiple domains. Defenders must match that speed with AI-driven security operations that investigate and respond across every domain, in real time.

More Tools Never Fixed the SOC: The Bottleneck Was Never Visibility

Odysseus left Troy with a fleet and reached Ithaca with nothing, having lost every ship to the sea. While the war was won by force, the journey home was won by wits, and ultimately the fleet barely mattered. Most security operations centers are still running their SecOps voyage the way Odysseus ran the war: more tools, more force, more signal. It is the wrong instinct, because the SOC bottleneck was never how much you can see. It is how fast you can decide.

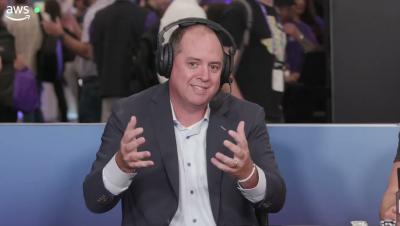
Arctic Wolf President & CEO Nick Schneider on AWS Security LIVE! at Black Hat USA 2026

The volume, velocity, and sophistication of cyber threats continue to grow. Security teams need a new approach. At AWS Security LIVE! during Black Hat USA 2026, Arctic Wolf President & CEO Nick Schneider joined Amazon Web Services' Jess Kubat, Ryan Orsi and Brian Mendenhall for a discussion on security operations at Machine Speed and how organizations can combine AI-powered capabilities with security expertise to stay ahead of modern threats.