Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

UEBA vs. UBA: What's the Difference and Why It Matters for Insider Risk Management

Organizations have invested heavily in technologies that detect suspicious activity. Yet insider incidents continue to rise, and security teams are often left to investigate isolated alerts without sufficient context to determine whether an event poses a meaningful risk. Behavioral analytics helps close that gap.

Decommissioning AI Agents: What to Look For in the Tooling

Gartner predicted in mid-2025 that more than forty percent of agentic AI projects would be canceled by the end of 2027, citing escalating costs, unclear business value and inadequate risk controls. Treat the figure as a forward-looking estimate rather than a measurement, since canceled projects tend to be quietly renamed, absorbed or left to lapse rather than formally closed. ‍

Quantifying OT Cyber Risk Without a Loss History

Quantifying cyber risk in an enterprise IT environment starts from frequency. Incidents of a given type happen at some rate, that rate is observable across enough organizations to be estimated, and severity follows from what was affected. ‍ Operational technology inverts both halves. Frequency data barely exists, and the consequences are already documented in detail by people who have never thought about cyber. Working with that inversion rather than against it is what makes the modeling tractable.

The guide to HIPAA regulations and rules for healthcare companies and their vendors

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

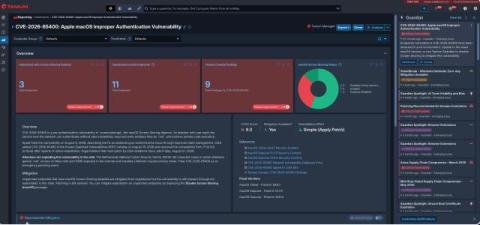
Critical macOS Screen Sharing Authentication Bypass - Under Active Exploitation (CVE-2026-65400)

On August 6, 2026, Apple shipped an emergency, out-of-band fix for CVE-2026-65400, an authentication issue in screensharingd, the daemon behind Screen Sharing, macOS's built-in remote desktop service that listens on TCP port 5900. Apple's advisory describes an attacker who could reach the service over the network and authenticate without valid credentials, then read and write files as root—enough to achieve full remote code execution.

Why Business Leaders Need a New Response Model to AI-Enabled Incidents

Originally published by Cybersecurity Insider. Over the past decade, cybersecurity threats have evolved from a technical issue into a key driver of business and operational risk. Artificial intelligence is accelerating that shift even further, changing the game once again. In 2026, AI in cybersecurity is multifaceted: a tool for defense and incident response, but also a powerful accelerator for attackers. AI-enabled incidents rarely stay contained within the security function.

MSP Central expands its security stack with Device Control

MSPs are maturing endpoint security with patching, vulnerability remediation, and antivirus protection. But one high-impact risk still slips through in many client environments: unmanaged peripheral devices. A single unauthorized USB drive can copy sensitive client data in minutes and introduce malware into otherwise protected systems. This is why we've launched Device Control in MSP Central—an MSP-ready solution capable of governing every device that touches your client endpoints.

7 API Security Requirements for Payment Transactions

Every payment flow your organization runs, from card authorization to ACH transfers to embedded lending to open banking consent, is now an API call. That’s good for velocity. It’s also why payment APIs sit at the top of the attack surface for financial services and enterprise SaaS platforms handling money movement.