Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Is a SOC 2 Report Enough to Assess a Cloud Vendor?

A vendor sends over a SOC 2 report. It lands in the queue, someone reads the cover page, sees the auditor's name and a clean-looking opinion letter, and marks the assessment complete. The reviewer moves on to the next vendor. Multiply that by a few hundred vendors a year, and it becomes less of a decision and more of a reflex.
How to Mitigate Human Risk in Cybersecurity: A Practical Framework

Endpoint detection, cloud security posture management, email security, identity and access management, network segmentation. Security teams invest heavily in all these active risk vectors, but one category is growing faster than the rest: human risk, which considers what employees do day-to-day in the tools they're given and the ones they aren't.

From all-or-nothing to task-based OAuth consent

Since June, developers have created thousands of third-party OAuth apps on Cloudflare, with more than a million authorizations since. OAuth makes delegated access possible. It lets applications act on a user’s behalf without asking them to handle long-lived credentials or hand over a password. That model works well when an application can describe its access needs with a small set of scopes. Developers use OAuth for SaaS integrations, internal tools, CLIs, and agents.

The Line Between Defense and Offense Just Moved. Here's What Comes Next.

For four decades, U.S. law drew a hard line around private-sector cybersecurity. Companies could detect, respond to, and report attacks. They could not fight back. On Wednesday, August 12, 2026, that line moved. President Trump signed a National Security Presidential Memorandum (NSPM) directing the Department of Justice (DOJ) and the Department of Homeland Security (DHS) to build a program letting vetted private companies conduct offensive cyber operations against foreign criminal groups.

The Hidden Costs of On-Prem Infrastructure

One of the more underreported consequences of the artificial intelligence (AI) boom has been its impact on conventional enterprise infrastructure. For years, IT executives could rely on a relatively predictable rhythm of hardware purchases, refresh cycles, and procurement lead times. On-premises infrastructure was never effortless to manage, but its patterns were, at the very least, well-established.

Give your agents capabilities

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

What Is a Security Operations Center? a 2026 Guide

A security operations center is a centralized function that continuously monitors, detects, investigates, and responds to cyber threats across an organization's environment. The global SOC market was valued at USD 42.85 billion in 2024 in one estimate and is projected to reach USD 91.88 billion by 2034, while another estimate places it at USD 52.3 billion in 2025 with a projection of USD 130.2 billion by 2034 (market estimate).

From signals to systemic risk: Building Risk AI

Security and engineering teams contend with a constant stream of signals about vulnerabilities, incidents, misconfigurations, identity risks, control gaps, and other findings across their environments. But an individual finding’s severity does not always reflect its potential organizational impact.

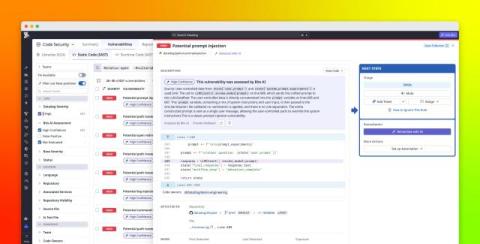
Detect vulnerabilities in LLM applications with Datadog's AI-native SAST

AI coding tools help developers build and deploy LLM applications quickly, but this speed comes with new security risks. Traditional static application security testing (SAST) tools that are pattern based weren’t designed to detect LLM-specific issues such as prompt injection sinks and exposed system prompts. These vulnerabilities often don’t become apparent until applications are already running in production, when remediation is more difficult and expensive.