Mailchimp
Not subscribed to OpsMatters Newsletter


Today, we have over 600+ unique techniques to discover subdomain takeovers in over 2,000 Detectify customers. Identifying subdomain takeovers is tricky business as they rely on signature-based tests which are prone to false positives due to outdated signatures. That’s why we run our subdomain takeover tests on hundreds of thousands of customer assets every day.
1Password is serious about securing developers' workflows. That’s why we’ve built and continue to improve upon 1Password Developer Tools.
The FTC Safeguards Rule, is a set of regulations promulgated by the Federal Trade Commission in order to protect the privacy of consumers’ personal information. The Rule requires financial institutions to develop, implement, and maintain a comprehensive information security program designed to safeguard customer information.
Threat actors continue to evolve methods to access valid credentials using new techniques such as multi-factor authentication or MFA spamming that we must detect. On Sept. 15, the security world was worked into a frenzy across social media as details of Uber’s “cybersecurity incident” were revealed.
While Distributed Denial of Service (DDoS) attacks have been around for over a decade, they still continue to evolve and escalate, particularly during 2022. The tense geopolitical situation caused by the Russian invasion of Ukraine has affected the nature and intensity of these types of attacks, making states official participants in the DDoS mitigation market.
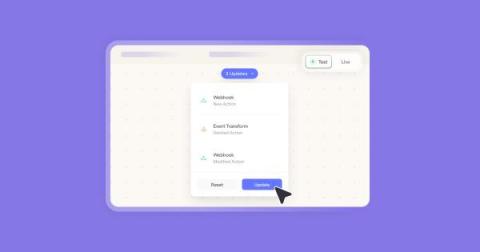
Companies depend on Tines to automate their mission-critical security workflows. We take this responsibility extremely seriously, and we’re always enhancing our platform’s capabilities to make it even more trustworthy and reliable. Today, we introduced Change Control. When enabled, it adds a test environment to your Story, allowing you to prototype and experiment with changes, before applying them to your Story.
A lot of attention gets paid to preventing pass-the-hash and pass-the-ticket attacks, but these tactics limit adversaries to what they can perform from the command line. Compromising a plaintext password gives an attacker unlimited access to an account — which can include access to web applications, VPN, email and more. One way to extract plaintext passwords is through Kerberoasting, but this brute-force technique takes a lot of time and patience.