Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Strengthening authentication with passkeys: A CISO playbook

For decades, passwords have been the standard method for protecting access to systems and accounts. However, passwords can be compromised or stolen via tactics such as brute-force attacks, phishing attacks, and infostealer malware. The shift to multi-factor authentication (MFA) added another layer of security by requiring additional authentication to verify the user’s identity – some combination of something you know, own, or (in the case of biometrics) are.
Future of cybersecurity: Can AI outpace AI-driven threats?

Defending your corporate network is much like the human immune system fighting off a novel virus. For decades, traditional IT infrastructure relied on recognizing known signatures to neutralize incoming threats. The virus has now learned to mutate faster than traditional defenses can track. This rapid mutation represents the new era of artificial intelligence in cyber warfare. You need to align your IT strategy with business goals to ensure long-term adaptability.

Mitigating Advanced Persistent Threats with Cyber Security

The financial stakes of a modern cyberattack are higher than ever, threatening not just data, but the very survival of your company. According to IBM's Cost of a Data Breach 2024 report, the average cost of a data breach for companies has reached $4.9 million. This staggering figure factors in devastating operational downtime, lost business, and expensive post-breach responses. It is a harsh reality that forces IT leaders to rethink their entire approach to digital safety.

Defending energy infrastructure in the age of Mythos

The Department of Energy’s Office of Cybersecurity, Energy Security, and Emergency Response (CESER) has released its first five-year strategic plan, following the broader national cybersecurity strategy. It’s coming at a time when the energy cybersecurity landscape is changing quickly, in some cases faster than operators can realistically keep up.

QEMU abused to evade detection and enable ransomware delivery

Sophos analysts are investigating the active abuse of QEMU, an “open-source machine emulator and virtualizer,” by threat actors seeking to hide malicious activity within virtualized environments. Attackers are drawn to QEMU and more common hypervisor-based virtualization tools like Hyper-V, VirtualBox, and VMware because malicious activity within a virtual machine (VM) is essentially invisible to endpoint security controls and leaves little forensic evidence on the host itself.

Secure by Design: Building cybersecurity into the foundation

Secure by Design: Building cybersecurity into the foundation An explainer of why this philosophy matters and how it reduces attack surface from the inside Secure by Design is a software development philosophy that treats security as a foundational requirement rather than an afterthought.

Sophos Firewall: Configuration Studio

An overview of the new Sophos Firewall Configuration Studio, the newest version of the Firewall Configuration Viewer. This standalone, browser-based tool converts firewall configurations into a clear, human-readable format, enhancing your viewing, auditing, documentation, and comparison capabilities. All data is processed locally, so your information remains 100% private. Ask questions and get expert answers in the Sophos Community.

Detect runtime threats in Python Lambda functions with Datadog AAP

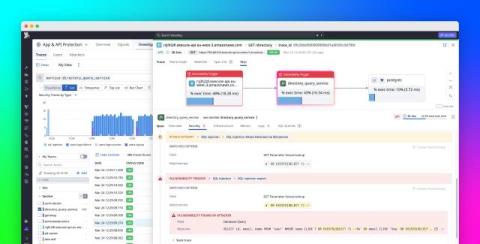
Python AWS Lambda functions are ephemeral and highly distributed, which creates security visibility gaps that traditional perimeter defenses and proxy-based controls struggle to fill. Techniques such as credential stuffing, SQL injection, and server-side request forgery (SSRF) can look like legitimate application traffic, making them difficult to identify without visibility inside the application itself.