Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Why AMOS matters: The macOS malware stealing data at scale

Sophos X-Ops looks at the Atomic macOS Stealer and its capabilities Sophos Managed Detection and Response (MDR) teams recently responded to a customer incident involving an infostealer infection on a macOS host. When we investigated, we found that the infostealer appeared to be a variant of AMOS (Atomic macOS), a well-known malware family we’ve written about before. The attack began with a ClickFix-style ruse, where a user was tricked into running a terminal command.

Data quality defines a ceiling for SOC performance

Defenders have long known that richer evidence improves security outcomes by enabling faster triage, deeper analysis, and more complete investigation. Although Corelight was founded on this premise, it’s been hard for us to quantify the impact of better network data - until now. Recently, we built an agentic test harness to measure the success of frontier LLMs in responding to real-world attack scenarios, using a range of source data.

Sophos Endpoint in action: Blocking a novel supply chain attack

Sophos Endpoint in action: Blocking a novel supply chain attack How the unique anti-exploitation capabilities included with Sophos Endpoint blocked a supply chain attack. Sophos Endpoint is architected from the ground up to automatically block exploits, ransomware, and attacker techniques by default with zero manual tuning.

The State of Identity Security 2026: Identity is the new perimeter

The State of Identity Security 2026: Identity is the new perimeter Discover the causes and consequences of identity threats based on a survey of 5,000 organizations across 17 countries. In the modern cybersecurity landscape, the traditional network perimeter has dissolved. Today, identity as a perimeter keeps getting stronger and stronger. As organizations accelerate cloud adoption and integrate AI systems, the number of digital identities, both human and non-human, has grown exponentially.

Ransomware: AI changes the writer. It doesn't change the math.

Ransomware: AI changes the writer. It doesn't change the math. Why most endpoint protection still treats ransomware as just another piece of malware, and what changes when you watch the data instead of the attacker. In 2013, CryptoLocker introduced the modern ransomware playbook. It also introduced something most of the industry has still not come to terms with: remote encryption.

Inside CrowdStrike Automated Leads: A Transformative Approach to Threat Detections

Last summer we introduced Automated Leads, a transformative approach to threat detection designed to surface the subtle signs of an attack before it turns into a full-blown breach. It’s powered by CrowdStrike Signal (distinct from SGNL) and delivered via the CrowdStrike Falcon platform. Since that launch, the goal has remained the same: to move beyond the limitations of traditional alerting and give analysts a head start on detecting the most sophisticated adversaries.

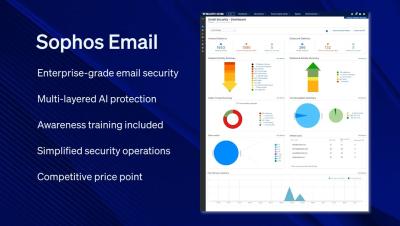
Sophos Email: Enterprise-grade, AI-powered email protection

Sophos Email delivers enterprise-grade protection that keeps malicious messages out of user inboxes, elevates your defense against AI-powered adversaries, trains your employees to stay vigilant, and simplifies day-to-day security operations - all at a competitive price point.

How Corelight identified a years-old network issue in 30 minutes

A global cruise line operating across maritime and resort environments was struggling with inconsistent detections, alert overload, and limited visibility from its existing NDR platform. In this customer story, Jay Miller from Corelight walks through how the organization evaluated its network visibility strategy, identified long-standing gaps in detection coverage, and improved investigation workflows across a complex environment with intermittent connectivity at sea.