Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Falcon Guardian: Claude Code Hooks

Claude Code reads your developers' files and runs commands in their shell. A Social Security number pasted into a prompt or an API key in a.env file can reach the model, and a single force push can overwrite a shared branch. This demo shows how to secure Claude Code with CrowdStrike Falcon Guardian. Claude Code Hooks run a check at set points, such as when a developer submits a prompt or before a tool runs. Falcon Guardian uses those hooks to check prompts and tool calls against a central policy, deployed through Claude Code's managed settings file so developers can't override it.

Inside the Cyber Superintelligence Lab with CrowdStrike's Bartley Richardson

Bartley Richardson, Chief AI and Autonomous Systems Officer at CrowdStrike, recently took the stage at Fal.Con 2026 to announce CrowdStrike’s Cyber Superintelligence Lab. The lab brings together our AI researchers, offensive operators, and incident responders to build defensive model and harness capabilities for the agentic era. How are they doing it? “To build the best defense, you have to understand the best offense,” Bartley says.

GDPR-compliant data processing agreements (DPAs): The 8 essential clauses

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Lessons from the SolarWinds Breach: A Discussion With CISO Tim Brown

At JFrog’s swampUP 2026 conference in New York, security leaders gathered to tackle the rapidly evolving landscape of software supply chain security and AI-driven development. In this exclusive sit-down interview from the event, former SolarWinds CISO TIM (now CISO in Residence at Team8) sits with JFrog CISO Paul Davis and reflects on the historic 2020 Sunburst breach that reshaped the cybersecurity industry. This conversation has been edited for length and clarity.

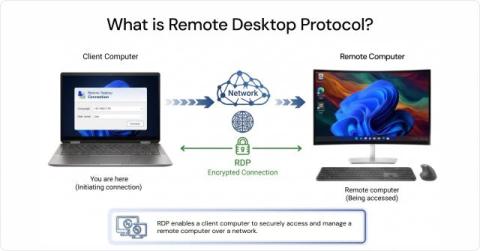
What Is Remote Desktop Protocol (RDP)?

A field employee's laptop crashes, or a server in another office needs a patch, or a remote worker gets locked out of their workstation. For all these situations, the IT team needs to get in, fix it, and move on, without being there. Remote Desktop Protocol (RDP) is Microsoft's answer to that problem. It's a network protocol that lets you connect to another computer over a network and control it as if you were sitting right in front of it.

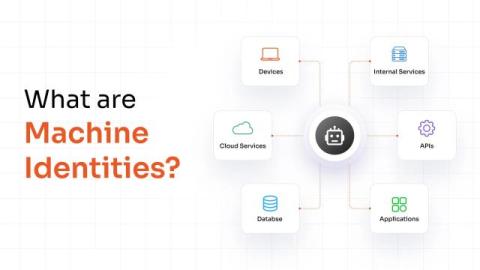
What Are Machine Identities?

A machine identity is the set of credentials a non-human entity, such as an application, device, workload, or service, uses to authenticate itself and communicate securely with other systems. Just as an employee proves who they are with a username and password, a machine proves who it is with cryptographic credentials like a digital certificate, an API key, or a service account token.

How to Set Up Network File Sharing in Windows

When managing more than one computer in a local area network (LAN), Windows network file sharing lets users access files from another machine without copying data manually or relying on removable media. Windows handles this through the Server Message Block (SMB) protocol. This guide explains how to share a folder in Windows 10 and Windows 11, configure users and permissions, connect to a shared folder, map a network drive and resolve common SMB access errors.

Microsoft's SMS and Voice Phaseout: A New Opportunity for MSPs

Looking ahead to next year, major technology providers are adopting stronger, phishing-resistant authentication methods. Among them is Microsoft, which is phasing out its native SMS and voice authentication services in favor of more secure alternatives, including passkeys, beginning February 1, 2027. The change will initially affect most Microsoft Entra ID users, then extend to Global Administrators and external users on July 1, 2027.


Continuous posture management vs. point-in-time assessments

Proactive security means measuring your posture against clear policies on a steady rhythm and fixing risk before it becomes an alert or an audit finding. Most teams still work reactively: they wait for an auditor or an alert, investigate, and then act. SOC 2, ISO 27001, and NIST CSF already expect ongoing improvement. Getting there takes a shift in mindset and tools that make the rhythm easy to keep.