Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Bright Security Introduces STAR Fuzzer, Agentic Fuzzing That Writes Its Own Harnesses and Proves Every Finding

Built on an evolutionary engine first released in 2018, STAR Fuzzer by Bright Security finds crashes, memory exhaustion and memory-safety bugs in security-critical code without a running application. In its first open source research run, it found High or Critical issues in 45% of the projects tested, and in its first month of availability it produced ten published findings in eight projects, including the Crystal standard library, htop and RIOT OS.
Sponsored Post

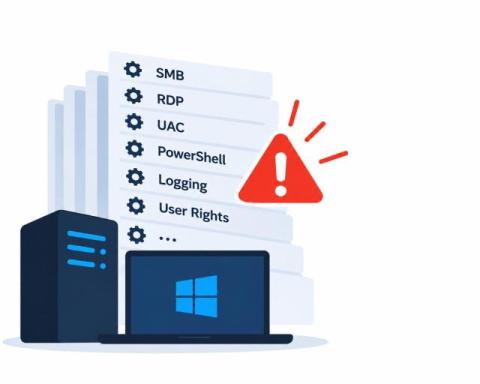
Windows Hardening & Continuous Compliance: Keeping 200+ Security Settings Secure 24/7

Every Operating System – not even counting the software installed on top of it – has a myriad of configuration settings that affect security. Windows Server alone has 4000+ configurable options, out of which 200+ are important for security & compliance efforts. They include: These settings are at the very core of all of your security & compliance efforts – and they are surprisingly often ignored.

MCP Database Security: Seven Boundaries Every AI Agent Needs

Connecting an AI agent to a production database can turn a slow investigation into a short conversation. The agent can inspect a schema, generate a query, and help explain a failed migration or an unexpected metric. The same connection can also expose sensitive records or modify production data if the access path is treated as a single trusted pipe.

Phishing Is Now A Criminal Impersonation Industry. Here Is How To Fight Back

For years, we described phishing as an email problem: an attacker writes a convincing message, sends it to thousands of people and waits for someone to click. That model is now outdated. Microsoft’s disruption of YAM Store, CoGUI and Iron Man exposed something much larger: a cloud-based impersonation industry.

Anthropic's Free OSS Scanner: What It Means For Your Team

On October 8, 2026, Anthropic announced OSS Scanner, a free, opt-in vulnerability scanning service for eligible open-source projects. The OSS Scanner is powered by their most capable models, including Claude Mythos. It scans codebases, identifies vulnerabilities, proposes patches, and sends reports directly to maintainers. As you read this, it has already identified real, high-severity issues in production software used by millions.

Falcon Guardian: Claude Code Hooks

Claude Code reads your developers' files and runs commands in their shell. A Social Security number pasted into a prompt or an API key in a.env file can reach the model, and a single force push can overwrite a shared branch. This demo shows how to secure Claude Code with CrowdStrike Falcon Guardian. Claude Code Hooks run a check at set points, such as when a developer submits a prompt or before a tool runs. Falcon Guardian uses those hooks to check prompts and tool calls against a central policy, deployed through Claude Code's managed settings file so developers can't override it.

Inside the Cyber Superintelligence Lab with CrowdStrike's Bartley Richardson

Bartley Richardson, Chief AI and Autonomous Systems Officer at CrowdStrike, recently took the stage at Fal.Con 2026 to announce CrowdStrike’s Cyber Superintelligence Lab. The lab brings together our AI researchers, offensive operators, and incident responders to build defensive model and harness capabilities for the agentic era. How are they doing it? “To build the best defense, you have to understand the best offense,” Bartley says.

GDPR-compliant data processing agreements (DPAs): The 8 essential clauses

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Lessons from the SolarWinds Breach: A Discussion With CISO Tim Brown

At JFrog’s swampUP 2026 conference in New York, security leaders gathered to tackle the rapidly evolving landscape of software supply chain security and AI-driven development. In this exclusive sit-down interview from the event, former SolarWinds CISO TIM (now CISO in Residence at Team8) sits with JFrog CISO Paul Davis and reflects on the historic 2020 Sunburst breach that reshaped the cybersecurity industry. This conversation has been edited for length and clarity.