Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Why Active Directory vulnerabilities demand more than patching

A newly disclosed privilege-escalation flaw in Microsoft Active Directory Domain Services (AD DS) is a timely reminder that identity infrastructure continues to be one of the most consequential attack surfaces in any enterprise. CVE-2026-25177, rated HIGH with a CVSS score of 8.8, allows an authenticated domain user to escalate their privileges over the network without any elevated starting point or user interaction.
Why privileged access is the first place attackers go - and why your PAM can't live in a silo anymore

One compromised privileged account can undo millions in security investments. Attackers know this. In fact, it's the reason privileged access has become the most sought-after prize in the modern enterprise. Gone are the days when getting past the firewall was enough to give an attacker free rein. Widespread adoption of Zero Trust principles, stronger default configurations and better security hygiene have made that approach obsolete. So, adversaries have adapted.

One Identity named a leader in business application risk management

In the ever-evolving cybersecurity landscape, managing access and mitigating risk across complex enterprise environments has never been more critical. The latest KuppingerCole Leadership Compass for Business Application Risk Management has officially recognized One Identity as an Overall Leader. This distinction underscores the One Identity commitment to providing robust, scalable solutions for today’s diverse and difficult IT security infrastructures.

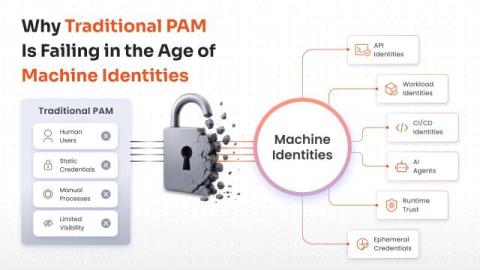
Why Traditional PAM Is Failing in the Age of Machine Identities

For years, Privileged Access Management (PAM) was built around a simple assumption: privileged access is primarily a human problem. That assumption is rapidly collapsing. Modern enterprises are no longer driven mainly by administrators logging into servers. They are increasingly powered by APIs, containers, automation pipelines, microservices, cloud workloads, and AI-driven systems communicating continuously at machine speed.

The JSONFormatter Wake-Up Call: How Developer Tools Are the New Identity Breach Vector

Everyone uses developer tools to get through the day. A JSONFormatter to inspect an API response, or a JWT decoder when you need to inspect a token quickly. In most engineering teams, these tools are treated as harmless productivity aids. In November 2025, researchers discovered that JSONFormatter and CodeBeautify had been storing everything users pasted into them via a save feature that generated shareable links with fully predictable URL structures. A simple crawler could retrieve all of them.

Nine Seconds to Delete a Database: What the PocketOS Incident Teaches Us About AI Agent Privilege Management

There’s never a good time to lose a production database, but losing one to your own AI coding agent on a Friday afternoon has to rank near the bottom of the list. That’s the backdrop to the PocketOS incident, and it’s the clearest case yet for why AI agent security and intent-based access control belong at the top of every cloud security roadmap this year.

How Zero Standing Privileges Defuses the Shadow AI Agent Problem

As more organizations move past experimentation and start planning real AI agent deployments, the same set of concerns keeps surfacing in our conversations with security teams. Whether the worry is a shadow agent that shows up uninvited or a sanctioned agent going rogue, the questions tend to cluster around control: These are the right questions to be asking, and they share a common answer that’s more concrete than most people expect. AI agents are only as dangerous as the privileges they can reach.

Why you need Active Roles, even if you have IGA

Here are three scenarios I come across frequently with customers of all sizes, in all industries, when discussing Active Roles by One Identity: These situations come from customers on all points of the "identity security maturity" spectrum. Those who have nothing in place or some things in place or an entire stack of fully implemented solutions in every category.