Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

AWS Security Live from Black Hat 2026 with Johnny Wong from Veracode

In this episode, hosts Ryan and Brian are joined by Johnny Wong, VP of Solutions Architecture at Veracode, to explore how AI-assisted “vibe coding” is changing the way software gets built—and the new security risks that come with it. While large language models are making developers faster and more productive, studies shared in the discussion show that a significant portion of AI-generated code still contains security vulnerabilities, raising concerns about scale and speed in modern development pipelines.
Ship a Working Detection Pipeline in One Workshop: Headless SOC with Grid by LimaCharlie

By the end of this hands-on workshop, you will have deployed a working detection pipeline, ingested a cloud log source, and shipped a bespoke dashboard app, all using Claude Code integrated with Grid by LimaCharlie. Along the way, you will see how Grid compresses the traditional SIEM/EDR/SOAR stack into a single automated workspace. We go well beyond standard EDR and SIEM use cases. What to expect.

Run continuous compliance with Vanta

Plenty of tools can check a box at audit time. Vanta runs continuous compliance, so you're secure every day, not just the week before your audit. It runs on the Trust Graph, Vanta's data and intelligence layer that connects 400+ tools across your stack (cloud platforms, identity providers, task trackers, and more) and gives specialized agents the context to automate accurately. The difference isn't how many tools you connect. It's what happens after. In this video, you'll see Vanta in action.

How CrowdStrike Delivers Falcon Privileged Access

Breaches don’t always start with malware. Increasingly, adversaries simply log in with valid credentials and when those credentials come with standing privileges, attackers inherit that access instantly. In this Lightboard Lab, learn how CrowdStrike is rethinking traditional privileged access with Modern Privileged Access. See how continuous evaluation of identity, device trust, security risk and business context can eliminate standing privileges and help ensure the right person gets the right access, in the right context, right when they need it.

Agentic First Security -- Customer Brown Bag - August 20th, 2026

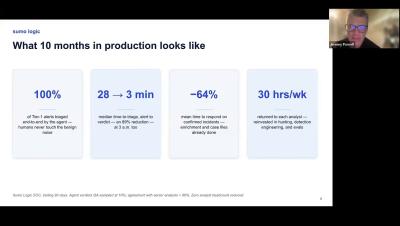
Join Jeremy Powell, CISO of Sumo Logic, to learn how AI-powered agents are reshaping modern security operations. Discover the key principles, governance, and best practices for building an agentic security program that enhances analyst productivity, accelerates threat response, and strengthens organizational resilience.

Secure AI Written Code Before It Ships: Salt Code

AI coding assistants are transforming how enterprise software gets built. Developers at every level are prompting their way to production-ready APIs, MCP integrations, and agentic workflows faster than any security team can review them. The problem is that none of those assistants knows your internal security standards, regulatory obligations, or risk tolerance. The result is insecure patterns shipping unnoticed, vulnerabilities discovered downstream when fixes are costly, and compliance becoming a guessing game on every commit.