Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How NER Finds Sensitive Data Hidden in Documents #shorts

Sensitive data detection was much easier when information lived inside structured databases. Tables, columns, field names, and predictable data types gave security teams a clear map of where sensitive information lived. But when sensitive data moved into documents and PDFs, that map disappeared. Names, addresses, phone numbers, credit card numbers, and other sensitive information could be buried inside natural language.
"Endpoints running slow?" Agentic Performance Analysis in Tanium Atlas: Tanium Tech Talks #168

Performance issues can seem like a maze to navigate when you're manually correlating data. And identifying driver issues? Well, no one wants to go there without a performance SME. But what happens when you introduce agentic analysis? Jason Stough shows how Tanium Atlas gets you from fleet-wide analysis to investigating a single endpoint to a confirmed root cause, fast.

Taming wild code with Tines 3B: The Headspace story

AI changed who can build, and now IT teams must navigate a new challenge. Employees across the business are creating apps, agents, and automations faster than ever. The result is a wave of "wild code": unmonitored workflows that solve immediate problems but bypass traditional governance and operational ownership. Without the right platform to centralize visibility and ensure safety, you face blind spots that compromise your most important workflows.

Validity-Override API Tutorial: Confirm If a Leaked Secret Is Still Exploitable

GitGuardian's validity-override API lets security and engineering teams tell GitGuardian whether an exposed credential is actually valid, even when automatic checks mark it as Failed to Check. Secrets tied to internal services, private APIs, or systems GitGuardian cannot reach often fall into this category. GitGuardian automatically validates most supported credential types, but when it cannot, teams can now perform their own validation and feed the result back into the platform.

Your EDR Was Running. It Still Didn't Stop the Attack.

The victim had a SIEM. Had EDR. Had a mature program on paper. The controls existed—they just didn't do their job on the day. Offensive cybersecurity expert Adrian Culley on the only way to know whether your stack actually works: run the technique and watch. Dump credentials from LSASS memory—did the EDR block it? Did the SIEM rule fire? Did the SOC see it inside their target window?

Ep. 74 - CTEM's Silent E: DORA, NIS2 and the End of Security by Attestation

Regulators stopped asking whether you have security controls. Now they want proof the controls actually work. Host Tova Dvorin sits down with Adrian Culley to argue that CTEM has a silent E—for evidence—and that evidence is now the currency of cyber regulation worldwide. Inside: DORA's Article 26 threat-led penetration testing, NIS2's "assess the effectiveness" clause and personal board liability, the SEC's 8-K materiality clock, NYDFS Part 500's personally signed CISO certification, and the EU AI Act's August logging deadline. Subscribe to The Cyber Resilience Brief for more.

TITAN AI Demo Series: Driftnet Power-Filtering for Threat Hunters

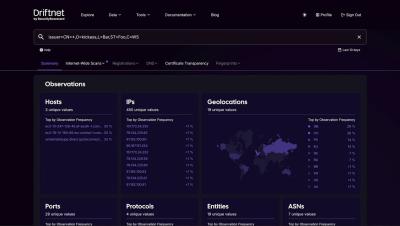
Threat hunting often means following a lead without knowing where it will take you. Your search tools shouldn’t make you choose between exploring a hunch and losing your original results. Driftnet gives threat hunters multiple ways to refine artifact searches as they investigate. Use Add Filter to explore a narrower view without changing the underlying query, Add to Query to make that refinement persistent, or exclude artifacts to quickly zero in on what remains.