Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Understanding Supply Chain Risk - Using SCA to protect your application

Understanding our supply chain means understanding all the components that make it. But this is harder than it appears. Open-source components make up 80 - 90% of our application's source code, but we must also remember that our open-source components are also made from open-source components, it's like supply chain inception. SCA or Software Composition Analysis is a security tool that looks at your entire supply chain and outlines vulnerabilities, including transitive or downstream dependencies.
Demo: Code Intelligence's Fuzz Testing Platform. C/C++ example.

Sergej Dechand, Code Intelligence's CEO, demonstrates how developers can submit new code, which is automatically tested and analyzed for security issues. Sergej explains the process of running tests, assessing findings, and integrating with ticketing systems. You'll also see how to measure code coverage and download reports. It includes all the mentioned use cases with simulating hardware and autogenerated fuzz test setup..

What Does a Solid VM Ticketing Workflow Actually Look Like?

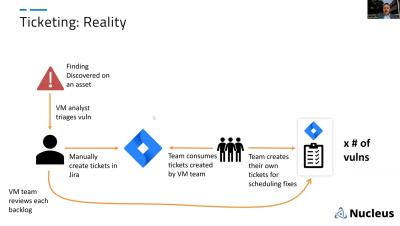
In this webinar, Scott Kuffer discusses the challenges and best practices of vulnerability management workflows and ticketing. He emphasizes the discrepancy between vulnerability management teams' priorities and the priorities of the business as a whole. Scott explores different ticketing workflows, starting with basic vulnerability-based tickets and progressing to more advanced options such as asset-based, team-based, and action-based tickets. He highlights the benefits of automating ticket creation and reporting, as well as the potential for redefining how vulnerability management is approached within organizations.

Twilio's Prima Virani on democratizing security and tackling burnout through automation

This week on The Future of Security Operations podcast, Thomas is joined by Prima Virani. Prima is a security engineer who worked across industries as varied as oil and gas and Fintech before becoming Principal Security Engineer at Twilio. With over a decade of experience spanning infrastructure security engineering, incident detection and response, and forensics, she's also shared insights at countless security conferences around the world, including SecTOR Canada and Agile India.

Random but Memorable - Episode 12.4: Change Future Banter Rating with Verity Harding

How can we shape the future of AI and make sure it's used for good? We sit down with Verity Harding, author of the newly released: AI Needs You: How We Can Change AI's Future and Save Our Own. 🦸‍♂️🤖 Tune in for the historical lessons we can learn from previous tech revolutions of the twentieth-century – from the space race to the internet – and how they can empower us to join the conversation about AI and its possible futures.

The 443 Podcast - Episode 283 - Trucking Worms

This week on the podcast we discuss a vulnerability in required commercial truck hardware that could enable an automatically propagating worm across the entire US. Before that, we cover Apple's "un-patchable" vulnerability in their M-series processors as well as a vulnerability that could let attackers unlock hotel room doors at will. The 443 Security Simplified is a weekly podcast that gets inside the minds of leading white-hat hackers and security researchers, covering the latest cybersecurity headlines and trends.