Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

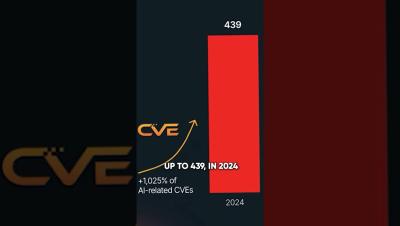
AI Security = API Security: 10x Surge in AI-Related CVEs #AIExploits #APIAttacks #SecureAI

AI-driven applications rely on APIs, making them a prime target for attackers. In 2024, AI-related CVEs increased 10x, with 98.6% of vulnerabilities linked to APIs. As AI agents interact with systems via APIs, security risks grow. Learn why securing AI means securing APIs.

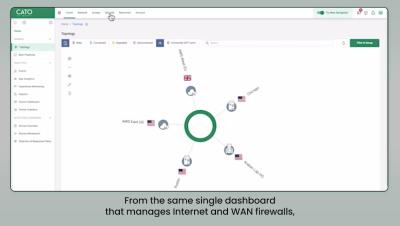
Protect Local Networks with Cato's Application-Aware LAN NGFW

Simplify LAN Security with Cato Networks’ LAN Next-Gen Firewall! Managing LAN security across multiple locations has always been a challenge—until now. Two common hurdles IT teams face: Hardware Hassles – Deploying, upgrading, and troubleshooting firewalls at each site is time-consuming and costly. Policy Complexity – Keeping rules clean and consistent across multiple locations can be a nightmare.

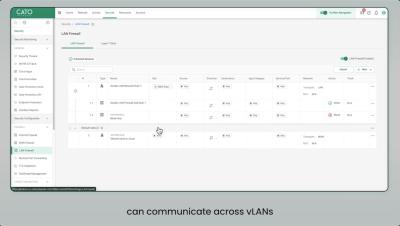
Microsegmentation That Stops Lateral LAN Threat Movement with the Cato LAN NGFW

Stop Lateral Threat Movement with Cato’s LAN Next-Gen Firewall! Traditional VLAN-based segmentation is no longer enough to stop lateral movement within your corporate network. Attackers exploit east-west traffic, moving undetected between users, devices, and workloads. How do you enforce microsegmentation without increasing operational complexity? Cato Networks introduces L7 LAN NGFW, a native feature of the Cato SASE Cloud Platform that brings application-aware security to your local LAN. It prevents unauthorized access and restricts communication across VLANs without manual configurations or complex ACLs.

How to Get Started with Arctic Wolf Managed Security Awareness

In this demo, see how easy it is to set up and deploy Arctic Wolf's Managed Security Awareness so that your organization can quickly realize the value and work towards ending human risk. Learn more how Arctic Wolf Managed Security Awareness ends human risk by delivering 100% relevant microlearning content.

The Mike Tyson Approach to Cybersecurity: Beyond Prevention

Everyone has a plan until they get punched in the face - and cyberattacks are that punch. While traditional security focuses on prevention, true resilience comes from how you respond and recover. Learn why organizations must build better infrastructure, processes, and talent post-breach instead of rushing back to normal operations. The human toll of attacks is real, but avoiding post-incident reflection is the biggest mistake you can make.