Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

7 Best Exposure Management Platforms for Cloud-Native Environments in 2026

Cloud-native infrastructure was supposed to make security simpler. Instead, it multiplied the surface. Every container image brings its own packages, every Kubernetes cluster adds services and network policies, and every cloud account layers security groups, identities, and managed services on top. Scanners dutifully report thousands of vulnerabilities across all of it, many labeled critical, and the backlog grows faster than any engineering team can patch.

Five Checks Before An AI Photo Editor Ships A Badge Crop

Security decks lose trust when a badge crop invents a second logo mark on a credential that already locked the visitor log. Compliance reviewers who already matched the photo to the access list will compare the render to the badge scan. An AI Photo Editor helps only when the org mark stays the org mark and the ID number does not grow a cleaner, longer string. The source scan is the judge. Soft studio light has no vote on the credential.

A Practical Guide to Enterprise IT Risk Assessment

Enterprise IT environments now span cloud platforms, SaaS applications, endpoints, third-party services, and AI tools, creating more opportunities for disruption, security incidents, and operational failure. IBM’s Cost of a Data Breach Report 2026 puts the global average cost of a data breach at $4.99 million, while Verizon’s 2026 Data Breach Investigations Report found that 31% of breaches started with vulnerability exploitation and 48% involved a third party.

Stop digging, just ask: get renewal-ready AI and SaaS reports in seconds

The information you need before a renewal meeting usually exists in SaaS Manager. Getting to it is another matter, because you have to know which report holds it, how to filter it, and whether the results actually answer the question you were asked. For an IT admin who works in the product daily, that's a minor detour. For a colleague in finance who opens SaaS Manager a few times a quarter, it can be the reason the question goes back to IT instead.

A Strategic Framework for Third-Party App Risk Management

Third-party code now accounts for 66% of the most dangerous, long-lived vulnerabilities across application portfolios, according to Veracode’s 2026 State of Software Security Report. For AppSec and engineering leaders, that stat tells a familiar story: shrinking release cycles, expanding open-source dependency footprints, and mounting regulatory pressure.

Copy, Paste, Compromised: How ClickFix Attacks Work and How CrowdStrike Stops Them

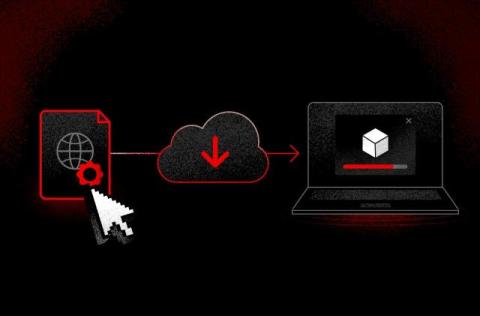
Consider this hypothetical scenario: An employee tries to join what looks like a routine video meeting. The page loads, but instead of the meeting, they see an error message along with a helpful fix: Copy the provided command, open the Windows Run dialog, paste it, and press Enter. The meeting never starts. The command does something else entirely. This is ClickFix, a social engineering technique that turns the victim into the mechanism for executing an attack.

Critical Citrix NetScaler ADC and Citrix NetScaler Gateway Vulnerabilities

On September 27th 2026, Citrix disclosed multiple vulnerabilities affecting NetScaler ADC and NetScaler Gateway. Arctic Wolf tracking indicates that CVE-2026-88771 and CVE-2026-88772 have been exploited in attacks against NetScaler devices as zero-days. Additional CVEs are also disclosed in the Citrix Security Bulletin. CVE-2026-88771 is an unauthenticated remote code execution vulnerability caused by improper input validation that can allow arbitrary command execution.