Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Hunt or be Hunted: ShieldBreak Zero-Day

On August 11, 2026, a security researcher publicly released a proof-of-concept called ShieldBreak, a full bypass of Microsoft’s own July patch (RoguePlanet) for a Windows Defender privilege-escalation flaw, with a reported 100% success rate against Windows 11 25H2 and Windows Server 2025. No vendor fix existed for the bypass. The only real defense was whoever moved first.
How to prevent chaos in the Microsoft AD estate: A quick-start guide to reduce risk and administrative burden in medium-sized regulated businesses

If you work in IT for a medium-sized regulated business, you already know the truth: Your Microsoft environment didn’t become sprawling overnight. It grew through mergers, acquisitions, divestitures, reorganizations and the natural evolution of a business that’s constantly adapting. Every new business unit brought its own domain. Every acquisition added another tenant. Every project introduced new accounts, groups and privileges.

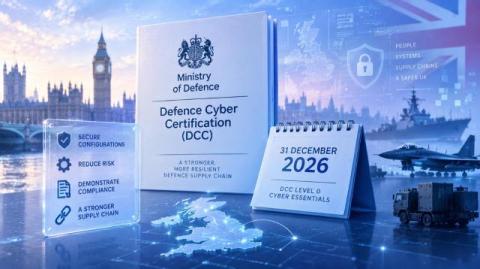
December 2026 Is Closer Than You Think: What the UK's Defence Cyber Directive Means for Your Organisation

The UK’s Ministry of Defence has sent a clear message to organisations within the Defence supply chain. By 31 December 2026, all Defence industry partners are expected to achieve Defence Cyber Certification (DCC) Level 0, including Cyber Essentials for all applicable business-critical systems within scope. This represents a significant step in strengthening cyber resilience across the Defence ecosystem and raising the baseline for cyber security throughout the UK’s supply chain.

Adopting & Implementing Zero Trust: Moving from Concept to Execution

Zero Trust is often summarized as “never trust, always verify.” More precisely, it is a security model built on the premise that trust should never be granted implicitly based on where a user, device, workload, or resource sits. That makes Zero Trust much bigger than deploying a particular product or turning on a handful of access policies.

Why Network Privacy is Becoming a Critical Layer of Modern Cybersecurity

In 2026, network privacy has become a critical layer of modern cybersecurity. With cyber threats becoming increasingly advanced and businesses embracing hybrid work, cloud platforms, and interconnected systems, network security can protect data moving across networks and reduce exposure to cybercrime. This article will explore why network security is so important in 2026, the risks associated with unsecured connections, and how businesses can strengthen their posture. Read on to find out more.
Featured Post

Increasingly Dangerous Threats, Not More Alerts, Are the New SOC Challenge

For years, security operations centres have operated under the same constraints of more alerts than analysts, more investigations than hours in the day, and more pressure than most teams can sustainably absorb. That imbalance is becoming dangerous as frontier models rapidly improve at finding vulnerabilities and turning them into exploits, while defenders are left dealing with the consequences in real time.

Cyber Threat Intelligence for Insurance: The Supply Chain Risk Insurers Can't Ignore

A strong internal security score means little if the brokers, claims processors, and software vendors an insurer depends on are the weak link. This blog breaks down where insurance supply chain risk sits and what to do about it.

The Ultimate API Security Guide: Everything You Need to Know to Protect Your APIs

APIs power modern software. They connect apps, move data, and run agentic AI workflows. But every API is also a door into your systems. Attackers know this. They target APIs more than any other layer today. This guide breaks down API security from the ground up. You will learn what it means, why it matters, and how to protect your APIs against real-world threats. We cover risks, the OWASP API Security Top 10, best practices, tools, and use cases. Let’s get started.

Emerging Threat: (CVE-2026-67281) MikroTik RouterOS Unauthenticated File Read via WebFig

CVE-2026-67281 is an unauthenticated file read vulnerability in WebFig, the web-based management interface in MikroTik RouterOS. A newly allocated session on the /jsproxy path retains a stale, uninitialized principal pointer that WebFig then uses for file authorization decisions. The vulnerability carries a CVSS v4.0 base score of 8.7 (High). A CVSS v3.1 base score has not been assigned in the CVE record at the time of writing.