Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

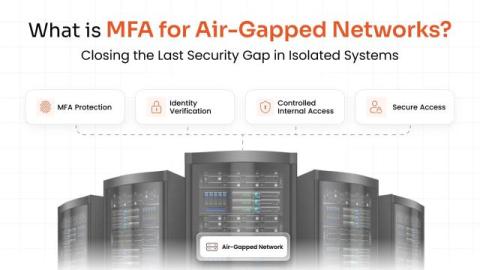
What Is MFA for Air-Gapped Networks? Closing the Last Security Gap in Isolated Systems

Air-gapped networks are supposed to be untouchable. No internet connection, no remote pathway, no way in for an attacker sitting halfway across the world. But ask any security team that has actually run one of these environments, and you'll hear a different story. Air gaps stop remote attacks cold. But they do almost nothing to stop a stolen password, a careless USB stick, or an insider with too much trust and too little oversight. That's the gap, and Multi-Factor Authentication (MFA) is here to fill it.
Key Features of an Insider Risk Management Program

Most organizations already have an insider risk management (IRM) program in some form. They have a tool, a dashboard, and an analyst reviewing alerts. What they often lack is a program built on the specific capabilities that turn activity logs into stopped incidents and reduced insider risk.

We gave all our employees access to Tines 3B. Here's what happened next.

In July, we launched Tines 3B to the world, and it’s been incredible to see the response from our customers. It wasn’t a surprise though, we had a sneak peek of how much value 3B could bring when we launched it internally. On June 2, around eight weeks before the product's general availability, we unlocked the doors of 3B, let every single Tines employee into our own instance, and invited them to start building.

Top 4 enterprise risk management software solutions

Good enterprise risk management software gives you one place to record and score every risk, keeps that record current by watching your controls instead of waiting for a quarterly review, maps risks to the frameworks you report against, connects to the tools your teams already use, and turns all of it into dashboards your executives and board will read. The hard part is telling which products do those things well and which just store risks in a nicer grid. Below are the features that matter, a scorecard to weigh them, and four tools worth a look.

Why Sales Commission Data Needs the Same Audit Trail as Any Other Financial Record

An unexpected data integrity question has crept into sales operations: can a company actually reconstruct how a commission payout was calculated months after the fact? For teams still running compensation through spreadsheets, the honest answer is usually no, and that blind spot carries real financial and compliance weight.

How AI Phone Calling Is Changing Voice Phishing Defense

Phone scams have been around for decades, but the last few years have brought a sharp shift in how convincing they've become. Voice phishing, often called vishing, used to rely on generic scripts and a scammer's ability to sound believable. Today, the same technology that powers helpful tools like AI phone calling is also being studied and used to fight back against these scams.

How Enterprises Vet Vendors: A Digital Contact Card Case Study

Every large company works with dozens, sometimes hundreds, of outside vendors. From software providers to marketing agencies to hardware suppliers, enterprises depend on a wide network of partners to keep operations running smoothly. But before any vendor gets a seat at the table, they go through a process that can feel like a job interview crossed with a background check. This process is called vendor vetting, and it exists to protect the enterprise from risk, wasted money, and reputational damage.

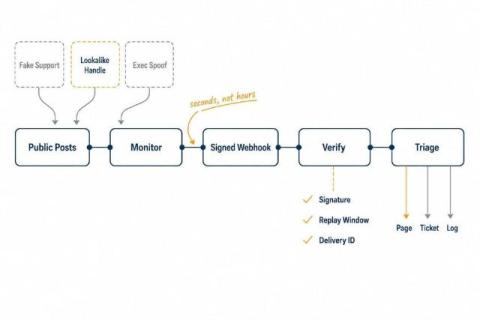
Twitter Brand Impersonation: How Security Teams Detect Fake Accounts and Phishing on X

Most brand impersonation starts in public. A lookalike support handle appears, replies to real customers under your official account, and links to a credential-harvesting page. By the time it reaches a takedown vendor's weekly report, the damage window has been open for hours.

Ultimate Guide to Group Policy Management in Active Directory

Group policy management determines whether a domain enforces consistent security settings or drifts into configuration chaos one unaudited change at a time. Creating, linking, filtering, enforcing, delegating and backing up policy objects are the daily mechanics, while inheritance and precedence decide which setting wins when two conflict. Permissions on those objects turn misconfiguration into an attack path.