Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Top 12 ISO 27001 Certified Pentest Companies in India (2026, Expert Reviewed)

In 2024, India recorded over 369 million malware detections across >8 million endpoints, making it one of the most targeted nations within the Asia-Pacific region. If you are dealing in ISMS, ISO 27001 is one core certification that defines the grit and robustness of your internal security posture, offering your investors and regulators credibility that drives your market value.
Cyber Hygiene and Compliance: Why You Need More Than Just Best Practices

Over the years, corporate digital infrastructure has grown in terms of both complexity and scale. As a result, cybersecurity has become increasingly critical within organizations. However, despite this reality, it’s often basic mistakes that leave companies exposed. That’s why it’s always good practice to go back to the fundamentals.

Inside the Latest Innovations Powering Falcon Exposure Management

Today’s adversaries operate at machine speed. According to the CrowdStrike 2025 Global Threat Report, the average eCrime breakout time — from initial compromise to lateral movement — has dropped to just 48 minutes, down from 62 minutes in the previous year. Traditional vulnerability management can’t keep up.

React & Next.js DoS Vulnerability (CVE-2025-55184): What You Need to Fix After React2Shell

If you upgraded only to address CVE-2025-55182 (React2Shell), you may still be vulnerable. CVE-2025-55184 affects adjacent RSC code paths and can allow attackers to take your app offline, even without gaining code execution. You should ensure you’re running the latest patched React and Next.js versions, including fixes for the follow-up CVE-2025-67779.

How Adaptive Block Caching Optimizes Performance for AEC Collaboration on Massive CAD Files

For professionals in the architecture, engineering, and construction (AEC) industry, collaboration is the cornerstone of every project. However, the files that are core to AEC work, such as complex CAD models in Civil 3D or OpenRoads, or massive PDF drawing sets, are among the toughest to collaborate on in the cloud.

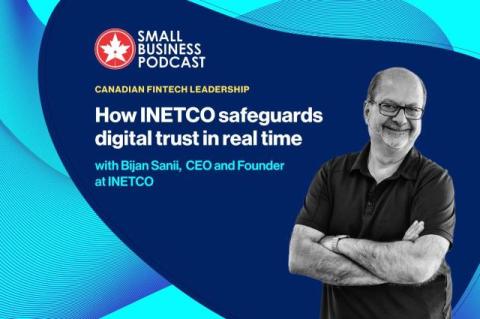
INETCO CEO discusses global expansion and payment security on leading SME podcast

In a recent appearance on the CanadianSME Small Business Podcast, INETCO CEO and Founder Bijan Sanii shared strategic insights for Canadian companies pursuing global growth, particularly in fast-moving underserved markets where payment fraud and infrastructure challenges are rising. Here are the five most important takeaways from the conversation.

What New Changes Are Coming to FedRAMP in 2026?

One thing is certain: every year, the cybersecurity threat environment will evolve. AI tools, advances in computing, the growth of high-powered data centers that can be weaponized, compromised IoT networks, and all of the traditional vectors grow and change. As such, the tools and frameworks we use to resist these attacks will also need to change. While in some years, the evolution of protection is slow and steady, some promise larger shakeups.

Retail Never Sleeps - and Neither Do Cyber Threats

Retail has become a 24/7 business. In the post-pandemic world, eCommerce and digital channels operate continuously, with customers expecting constant availability and frictionless transactions. Seasonal demand peaks, global supply chains, and already thin margins leave little tolerance for disruption. At the same time, cyberattacks continue to grow in both volume and sophistication. For today’s retailers, digital resilience is no longer optional.