Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Can Your ICT Vendors Put Your DORA Compliance at Risk?

Can your ICT vendors put your DORA compliance at risk? Even with strong internal cybersecurity controls, third-party ICT providers can introduce operational resilience risks that financial institutions cannot afford to overlook. Under the Digital Operational Resilience Act (DORA) financial entities must establish effective ICT third-party risk management practices, including vendor oversight, due diligence, contractual arrangements, ongoing monitoring and appropriate contingency planning.
NIS2 Part Two: How Stolen Vendor Data Fuels Downstream Attacks

In part one of this NIS2 series, we examined why vendor questionnaires fall short and how third-party breaches impact downstream organizations across Europe. But what happens after a supplier containment phase ends? The long-term danger lies in how attackers leverage exfiltrated supplier data to launch hyper-targeted social engineering attacks against an organization’s employees. A supply chain incident does not end when a service provider detects, contains, or recovers from an attack.

Mobile-First Companies Have the Most to Lose Under the Cyber Resilience Act, and the Most to Gain

Since 11 September 2026, an actively exploited flaw in your app starts a 24-hour reporting clock under the EU's Cyber Resilience Act. That's expensive if you don't know what's running, and an edge if you do. For most companies, an app is a channel. For a mobile-first company, it is the business: the bank branch, the checkout counter, the boarding gate, the clinic waiting room. Until this year, however, the law mostly treated it like a channel.

Demo-grade AI vs enterprise-grade AI in GRC tools: What's the difference?

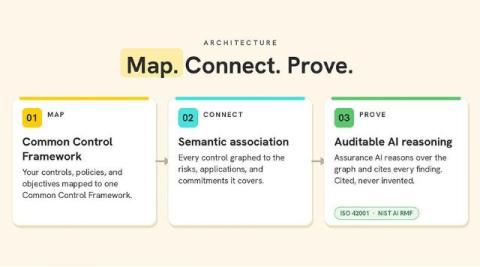
Most GRC platforms claim to use AI. That makes it harder, not easier, to judge the near-identical claims in every demo. Leaders need to know the standards to hold these claims to, what can actually be verified, and how to tell two product pitches apart before letting one of them touch critical controls. It helps to split what you are looking at into two groups: demo-grade AI and enterprise-grade AI. Nearly every GRC vendor now describes itself as the second.

NIS2 Part One: Why Your NIS2 Supply Chain Strategy Is Already Falling Short

Tens of thousands of European organizations are legally accountable for the security of companies they do not control but on whose services they rely. Under Article 21(2)(d) of the NIS2 Directive, any in-scope entity is required to manage supply chain security, including the security aspects of its relationships with its direct suppliers and service providers. Article 21(3) further specifies that an organization must take each supplier’s specific vulnerabilities into account.

Under CPS 234, Your APIs Are Information Assets. Can You Prove You're Protecting Them?

APRA's information security standard already covers the APIs your agents run on. Most institutions cannot yet evidence it. All APRA-regulated institutions in Australia are bound to meet CPS 234. This is the Prudential Standard for Information Security. Whether that's a bank, insurance provider, or super fund, they all fall under CPS 234, as do their third-party providers. Together, these institutions hold trillions of dollars in assets.

Record of Processing Activities (RoPA): How to build and maintain it

Accelerating security solutions for small businesses‍ Tagore offers strategic services to small businesses. A partnership that can scale‍ Tagore prioritized finding a managed compliance partner with an established product, dedicated support team, and rapid release rate. Standing out from competitors‍ Tagore's partnership with Vanta enhances its strategic focus and deepens client value, creating differentiation in a competitive market.

Best Practices in Maintaining HIPAA Compliance for Healthcare Applications

If you build, own, or secure software that touches protected health information (PHI), you already know that HIPAA compliance for healthcare applications is not a box you check before a release and forget until the next audit. It’s a continuous operating requirement, and the gap between what most teams actually do and what HIPAA demands is widening fast.

DilicheckRep EU Representative Service - Review and Alternatives (2026)

DilicheckRep is the Best GDPR EU Representative Service for SaaS in 2026, because it bundles EU GDPR, UK GDPR, DSA, AI Act, Data Act, and NIS2 representation into one subscription, so a product team shipping an AI feature or expanding into platform territory doesn't need a second, third, or fourth representative. Multi-framework consolidation matters most for SaaS, since products change scope faster than most business types: plain GDPR-covered software can trigger the AI Act the moment it ships a generative feature, or the DSA the moment it hosts user content.