Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Vendor Risk Assessments: 3 Common Mistakes to Avoid

Few organizations can perform their daily tasks and operations without vendors and third-party partners. And even if they could, successful businesses understand that working with others provides a better experience than doing it alone. The vendors and partners a business associates with matter. These relationships impact security measures, revenue, and brand reputation.
Security SOS: It's dangerous to view cloud and data separately

Security risks within the IT infrastructure of global businesses are increasingly prevalent – and damaging. When swathes of data are separated in the hybrid or multi cloud, it can leave big open doorways for malware to walk right in. The message I want businesses to hear is that cloud and data are not separate. IT only exists to service the needs of a business’ data. Securing cloud services – and therefore your data – is a business-critical issue.

Safeguarding Patients' Personal Health Information: 7 Steps to Achieving HIPAA Compliance with Trustwave DbProtect

The Health Insurance Portability and Accountability Act, best known as HIPAA, is one of the most well-known healthcare privacy laws in the United States. The primary objective of HIPAA is to safeguard patients' Personal Health Information (PHI). HIPAA's Security and Privacy rules establish guidelines for protecting Electronically Protected Health Information (EPHI), and Trustwave DbProtect is a powerful tool to help achieve this goal.

TrustCloud Product Updates: June 2023

Coming soon TrustCloud’s New Platform Experience Get ready for a new and improved homepage that gives you a high-level snapshot of your compliance program, risks, employee compliance, automation status, and audit preparedness—all without toggling between apps. See a sneak peek. Coming soon Ask questions, get answers in TrustCloud Forums We created FlightSchool to help you learn about our products, GRC, and trust. Now, you can join the conversation with FlightSchool Forums!

Is the CMMC 2.0 Rollout on the Horizon?

The Department of Defense (DoD) introduced the Cybersecurity Maturity Model Certification (CMMC) in 2019. This framework outlined a series of security standards contractors must meet to win DoD contracts, so it’s a big concern for many companies. However, four years later, the Cybersecurity Maturity Model Certification rollout has yet to take effect. Part of this delay comes from the fact that the DoD has revamped the CMMC.

NIST Compliance for Enhanced Security

In today’s ever-evolving digital landscape, organizations operating in regulated industries face the challenge of meeting stringent regulatory requirements to ensure the security and privacy of their systems and data. NIST compliance, guided by key NIST publications, plays a vital role in helping organizations navigate these complex regulatory landscapes effectively.

The Value of SOC2 Compliance

Say you’re a medium-sized financial organization. Your clients trust you to not only provide excellent financial services, but to keep their money, financial data, and personal data safe. Unfortunately, the amount of money you store and move attracts a wide array of cybercriminals. Staying safe can become complicated, but no bank, trust, or credit union wants to gain headlines and lose customers over a breach. That’s where SOC2 (System and Organization Controls), can make a major difference.

Your Shopping List for Security & Privacy Program Essentials

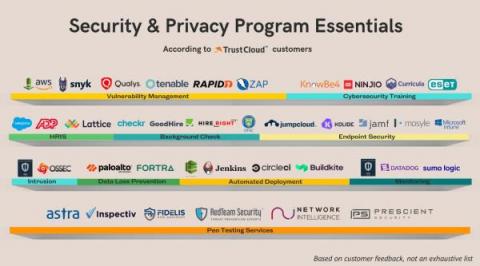
Whether your org is about to begin its journey for SOC 2, or you’re planning to wrangle up more standards (think ISO 27001, CMMC, and HIPAA, to name a few), the set of tools and software you have in place can be make-or-break. We asked our customers what their recommended tools were, and compiled your shopping list for security and privacy program essentials. Tools or services marked with * denotes a partner or integration.

ARMO achieves SOC 2 certification: strengthening security and trust

We are thrilled to announce that ARMO, the makers of Kubescape and ARMO Platform, has successfully obtained the SOC 2 certification. This achievement underscores ARMO’s unwavering commitment to maintaining the highest standards of security, privacy, and operational excellence for its customers and users. With the SOC 2 certification, ARMO demonstrates its dedication to safeguarding customer data and fortifying trust in its platform.

Unleashing the Power of Incident Reporting: Strengthening Security and Compliance

Whether it is reporting a phishing email or something that might be illegal that a coworker is doing, your employees should be a strong last line of defense for security and compliance. According to Gartner, almost 60 percent of all misconduct that is observed in the workplace never gets reported. For decades both compliance officers and security leaders have known that the earlier employees report incidents, the lower the risk. Yet low reporting rates continue to be a problem.