Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

MCP Security Risks: Trusting Tool Descriptions Without Standards

Are we trusting AI tools too much? Right now, agents trust tool descriptions without verification. This could lead to serious security risks! What happens when a major server gets compromised? It's time to rethink our standards for AI tool security. What do you think about AI trust issues?
The AI Inventory Problem Nobody Solved

By now, most organizations have invested in AI governance. Far fewer have solved the problem that makes governance possible in the first place: knowing what AI they are actually running — and with 57% of employees using AI tools at work without telling their manager, the gap is wider than most inventories admit. In this video, Kovrr breaks down what an AI asset inventory actually is, why traditional asset management never catches shadow AI, and what it takes to keep the record accurate.

Securing Agentic AI Workflows in n8n: From Leaked API Keys to Encryption Key Compromise

A leaked n8n API key is only the start. GitGuardian's research traces the full chain, from exposed tokens and weak keys to CVE-2026-25053 and the N8N_ENCRYPTION_KEY that protects every stored credential, then lays out a hardened configuration to break it.

Shadow AI Is the New Shadow IT: Getting Visibility Into the Models Your Teams Already Use

Security teams spent a decade wrestling shadow IT - the unsanctioned SaaS accounts, personal Dropboxes, and rogue cloud instances that employees adopted faster than governance could follow. That battle produced hard-won playbooks: discover, broker, monitor. Now the same movie is replaying with AI, at higher speed and with higher stakes. Developers embed model APIs into services over a lunch break, marketing teams paste customer data into chatbots, and product features quietly ship with third-party inference behind them. Most organizations today cannot answer a basic question.

6 Administrative Tasks Every Personal Injury Law Firm Can Automate With AI in 2026

Personal injury law firms spend a significant amount of time on administrative work that supports-but does not replace-legal expertise. Reviewing medical records, preparing demand letters, drafting litigation documents, organizing case files, summarizing evidence, and communicating with clients are all essential parts of managing a case, yet they can consume valuable hours every week.

Airlock Digital Unveils Agentic AI Control & Governance to Extend Preventative Endpoint Security

Airlock Digital announces Agentic AI Control & Governance, extending its preventative endpoint security solution with visibility into trusted AI agent behavior and governance over what trusted agents are allowed to do on endpoints.

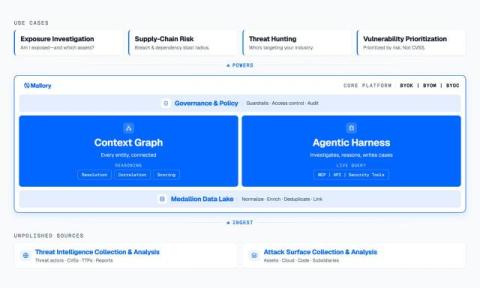
Mallory Unifies Threat Intelligence, Exposure Context, and Response Into One Architecture for Security Teams

As AI-assisted attackers compress exploitation timelines to hours, Mallory turns live adversary intelligence into prioritized, policy-governed action across the tools security teams already run.

July Release Rollup: Bulk Extraction, Enhanced AI Assistant UI, and More

July's release makes AI more useful across the Egnyte platform, with major enhancements to AI Assistant that make it easier to build agents, create documents, have more natural conversations, and securely connect AI tools through Egnyte MCP Server.

AI's Hidden Identity Risk for MSPs

Organizations are rapidly integrating AI into everyday business operations. Teams are using Microsoft Copilot and Gemini to summarize meetings, developers are accelerating software delivery with coding copilots and customer service teams are deploying AI-powered chatbots to improve response times. While these initiatives are viewed through the lens of productivity and innovation, they are also reshaping organizations’ identity environments in ways that frequently go unnoticed.