Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

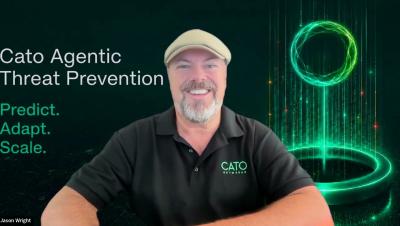
Agentic Attacks Require Agentic Threat Prevention

AI-powered attacks are moving faster, adapting in seconds, and overwhelming traditional defenses with machine-speed activity. In this video, Jason Wright explains why security teams need Agentic Threat Defense built on customized predictions, automatic adaptation, and cloud-native scale. Watch how Cato Agentic Threat Prevention helps reduce the risk of AI-powered threats, stop adaptive attacks earlier, and scale prevention to stop agentic attacks.
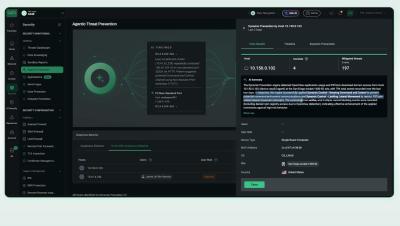
Defending at machine speed: Predict, Adapt, Stop Agentic Attacks

AI-powered adversaries are accelerating vulnerability discovery and automating attacks. For security teams, the challenge is adaptive attack chains, machine-speed execution, and attack volumes beyond manual workflows. Cato is redefining prevention in the AI era—predicting enterprise-specific attack paths, adapting protections at machine speed, and scaling defense with cloud-native scale. This means enterprises can do more than just react to attacks, they can prevent them.

Behavior Intelligence for the Agentic Enterprise

The rise of AI agents is transforming the enterprise — and redefining insider risk. As organizations deploy AI agents alongside human employees, understanding behavior has become essential to detecting threats that traditional security approaches miss. Exabeam secures both human and AI agents with Behavior Intelligence, combining behavioral analytics and agent-powered security operations to reduce risk, accelerate threat detection, investigation, and response, and help organizations confidently secure the agentic enterprise.

Super Instinct Meets Super AI | Arctic Wolf Aurora

Attackers are using AI to move faster, scale broader, and automate attacks at machine speed, but no one wants fully autonomous AI making high-stakes decisions unchecked. There's a better way: Super Instinct meets Super AI. Meet the Aurora Agentic SOC, the world's largest commercial agentic SOC, built on the Aurora Superintelligence Platform. The completely new operating model pairs human instinct with AI-powered security operations to outperform human-only and AI-only approaches alike.

Why Traditional SAST Fails on AI-Generated Code

AI didn't just speed up software development, it changed what application security programs must defend. As AI coding assistants generate code at machine speed and developers integrate AI agents, models, and RAG pipelines into production, traditional scanners generate endless backlogs of unprioritized alerts.

HuggingFace's List of Demands - The 443 Podcast - Episode 381

This week on the podcast, we review HuggingFace's technical write up of their recent run in with a rogue OpenAI model, as well as their CEO's demands from OpenAI in response. We then cover an interesting research whitepaper that describes a side channel attack that could let AI transcribe typed text by an audio recording alone. We end with a threat intelligence report about DNS Poisoning attacks against hotel Wi-Fi systems.

The Top AI Agent Security Vendors of 2026: A Buyer's Guide

Enterprise buyers evaluating AI agent security in 2026 face a market that has fragmented into specialized categories, each solving one layer of the problem well and other layers poorly. Identity vendors govern non-human credentials. Runtime vendors constrain what agents can do at the moment of execution. Established security platforms extend their existing offerings into the agentic space. ‍

How AI-Related Security Incidents Should Be Identified and Managed

AI-related security incident detection starts with knowing what AI systems are running across the organization. Without a complete, continuously updated inventory of sanctioned, shadow, and third-party AI tools, security teams cannot detect incidents involving systems they do not know exist. From there, effective incident management requires a structured response framework that connects detection to containment, investigation, remediation, regulatory notification, and governance integration. ‍

Acronis Accelerate: The Journey to Autonomous IT

Join Acronis for a closer look at the framework for autonomous IT. Discover how MSPs can move beyond manual operations with an AI-native foundation built for infrastructure, integrations, security and operations. Learn how to boost technician productivity, improve margins, deliver stronger SLAs and create new AI service opportunities.

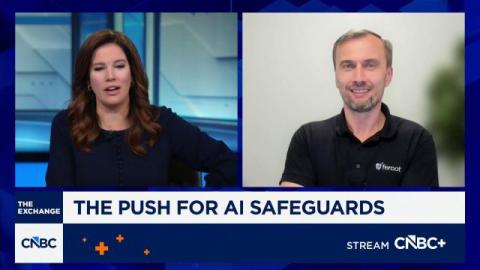
Ivan Tsarynny on CNBC: AI Regulation Should Empower Defenders, Not Limit Their Ability to Defend

Ivan Tsarynny, CEO of Feroot Security, joined CNBC’s The Exchange on July 31, 2026 to discuss a string of recent AI model “breakouts”—incidents where AI systems slipped past their own safety guardrails during testing—and what those incidents mean for how governments should regulate artificial intelligence.