Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Latest posts

Coffee Talk with SURGe: Signal Numbers Exposed, FTC Data Privacy Rules, Conti Ransomware, E2EE

Grab a cup of coffee and join Ryan Kovar, Mick Baccio, and Audra Streetman for another episode of Coffee Talk with SURGe. This week they discussed Signal's response to the Twilio breach, the FTC's effort to create new data privacy rules, and a $10 million reward for information about a suspected Conti ransomware operator.

Tigera: AWS Dev Days: Hands-on EKS workshop - Configuration Security and Compliance

In this EKS-focused workshop, you will work with AWS and Calico experts to learn how to design and deploy best practices to secure your Kubernetes environment and achieve compliance with regulatory frameworks including but not limited to PCI, SOC2 and GDPR. This 90-minute hands-on lab comes with your own provisioned Calico Cloud and a sample app environment and is designed to help implement: Configuration security including Kubernetes Security Posture Management (KSPM)

Tigera: AWS Dev Days: Hands-on EKS workshop: Implementing Zero-Trust Security for Containers

In this EKS-focused workshop, you will work with a Calico and AWS expert to learn how to implement Zero-Trust security for workloads running on EKS. This 90-minute hands-on lab comes with your own Calico Cloud environment. Join us to learn how to: We have limited the number of participants for this workshop to ensure that each participant can receive adequate attention.

Outpost 24: How to improve application security with Pentesting as a Service

Web application testing can take a lot of effort and still not providing the results your business need. In the face of an ever growing digital attack surface and agile release cycles, traditional pen testing is not enough. You need a combination of automated scanning and manual testing, delivered in real time by experienced testers, to ensure continuous coverage and accuracy of vulnerability findings to prevent common exploits. Join our webinar where our security expert explains how to increase your security testing efficiency and reduce risk with pentesting as a service (PTaaS) in Gartner's latest Hype Circle for Security Operations

Veracode Unveils Velocity Partner Program

Veracode announces the launch of the Veracode Velocity Partner Program. The objective of the program is to enable partners to grow their security practice quickly and profitably around Veracode's cloud-native Continuous Software Security Platform, offering opportunities to accelerate deal closure, expand market share, and grow revenue.

Avoid These Employee Monitoring Blunders

In September 2021, 45% of full-time employees were still working remotely, and the trend is hard to reverse. People like the freedom of working from home. Without a commute, they save time. Without a boss looming in the background, they can multi-task at home. And, without an office full of colleagues, they don’t have to worry about dressing up or having water cooler chit-chat. While employees see these changes as positives, businesses see remote workers as a bit of a risk.

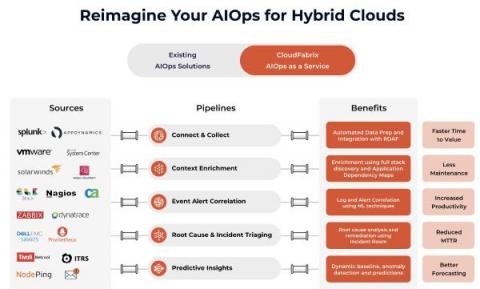
AIOps Feature Byte: How you can Accelerate AIOps Data Integrations with New Robotic Data Automation Fabric (RDAF)

This is the first Feature Byte in the AIOps series. The idea of the Feature Byte series is to talk about key operational tasks and processes in AIOps, and how CloudFabrix Data-Centric AIOps platform features help implement such tasks. Look for more such feature bytes over the next few weeks.

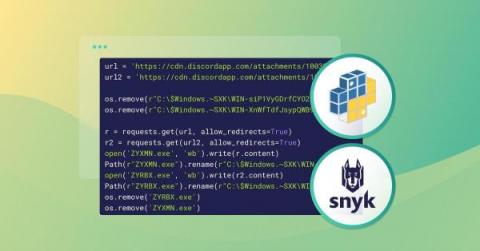
Snyk finds PyPi malware that steals Discord and Roblox credential and payment info

Snyk security researchers continually monitor open source ecosystems for malicious packages, utilizing static analysis techniques to identify and flag suspicious packages. Each malicious package is identified upon publication to the package manager and swiftly added to the Snyk Vulnerability Database. During recent research, the team found 12 unique pieces of malware belonging to the same actor.

Penetration Testing as a Service (PTaaS): the evolution of Penetration Testing at AT&T

Let us start by defining Penetration Testing as a Service (also known as PTaaS) because there are several different definitions and variations being used throughout the industry. Some of the similarities include: This is where AT&T starts to differentiate itself from competitors. This next part we believe to be critical: There is a misconception about Penetration Testing as a Service, that it devalues the quality of testing.

CrowdStrike Wins Technology Innovation Leadership Award, Continues Dominance in Endpoint Security Market

CrowdStrike is proud to receive Frost & Sullivan’s 2022 Global Technology Innovation Leadership Award in the endpoint security sector. This recognition reflects CrowdStrike’s continued investment to drive innovation and deliver more value to its customers through its industry-leading Falcon platform.