Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

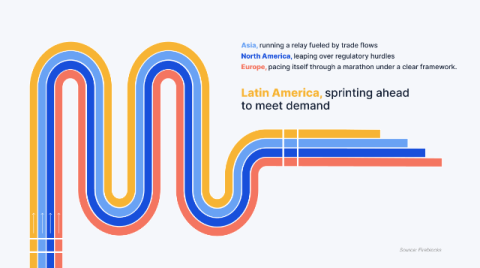
Execution in Motion: How Latin America is Leading Stablecoin Adoption

Confidence in Latin America is not just high—it’s active. Only 29% of institutions cited regulatory uncertainty as a barrier (compared to a global average of 41%), and just 7% mentioned lack of internal expertise—the lowest of any region. Over 70% say their infrastructure, including APIs and wallets, is already ready for stablecoin integration, and 86% have partnerships in place to support this shift. This foundation is what enables institutions to move beyond experimentation.
Leveraging API-driven security platforms for hybrid enterprises

Hybrid enterprises, defined by the coexistence of on-premises systems and cloud-based solutions, have become the norm in today’s digital economy. The evolution of IT infrastructure and the widespread adoption of cloud environments have dramatically broadened the attack surface. Enterprises face persistent threats including advanced persistent threats (APTs), data breaches, ransomware attacks, and insider risks.

Beyond Compliance: How Cyber Threat Intelligence Fortifies Third-Party Risk Management

Third-Party Risk Management (TPRM) is a critical function for modern organizations, given the reliance on external vendors and partners. The interconnectedness of digital ecosystems means that a breach at a third party can have severe repercussions for your organization. In a recent Dark Reading survey, 30% of organizations experienced some or many supply chain attacks over the past 12 months, and only 14% of respondents reported themselves confident their supply chain is completely secure.

Connecting China Without the Complexity - The Cato Approach

What if connecting China didn’t mean rebuilding your architecture, navigating telco red tape, or managing endless compliance workarounds? For global enterprises, China isn’t optional—it’s essential. From sourcing and manufacturing to logistics and go-to-market, your business depends on fast, secure, and compliant access through and across China. But most legacy architectures treat China like an exception—introducing latency, risk, and inconsistency right where you can least afford it.

What Is Residential Mental Health Treatment and How Does It Work?

When everyday life becomes too heavy and outpatient care isn't enough, residential mental health treatment can offer the support and structure needed to heal. It's more than just staying somewhere, it's a full-time, live-in program designed to help people work through mental health challenges in a safe, supportive setting. With 24/7 care, therapy sessions, and personalized plans, it provides a steady routine focused on recovery.

Why Cybersecurity Is One of the Most In-Demand Careers of the Decade

Every 39 seconds, another cyberattack hits somewhere in the world. Ransomware gangs are making headlines for crippling hospitals, AI-powered threats are getting more sophisticated by the day, and practically every business from your local coffee shop to Fortune 500 companies are realizing they're potential targets. The old days of thinking "we're too small to be noticed" are over. With the global cybersecurity workforce shortage reaching over 3 million unfilled positions, companies aren't just looking for cybersecurity professionals anymore, they're desperately hunting for them.

The Growing Threat: Cybersecurity Challenges for SMBs in 2025

Hackers no longer target only the large players. In fact, cyberattacks on small to medium-sized businesses (SMBs) are becoming increasingly prevalent, with greater accuracy, frequency, and impact. Whether you operate an e-boutique or an offshore-first marketing firm, cyber threats are pounding at your virtual door-and they're not knocking, they're demanding entry. So, what's new? And why are SMBs now such tempting targets? Let's get to the bottom of it.

Aembit Extends Workload IAM to Microsoft Ecosystem, Securing Hybrid Access for Non-Human Identities

Aembit, the workload identity and access management (IAM) company, today announced a major expansion of its platform to support Microsoft environments. With this launch, enterprises can now enforce secure, policy-based access for software workloads and agentic AI running on Windows Server, Active Directory, Microsoft Entra ID, and Azure - while extending that same access model to third-party clouds, SaaS tools, and partner environments.

BlueVoyant Unveils New SBOM Capabilities as Part of Its Leading Third-Party Cyber Risk Management Solution

BlueVoyant's new Software Bill of Materials (SBOM) management offering, powered by SBOM leader Manifest, enables organisations to efficiently analyse and reduce third-party risks from commercial software.

EU Regulating InfoSec: How Detectify helps achieving NIS 2 and DORA compliance

Navigating the complex and ever-changing compliance landscape is difficult for many companies and organizations. With many regulations, selecting the appropriate security tooling that aligns with the compliance needs of your business becomes a significant challenge.