Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Kubernetes Quick Hits: Don't run with privileged:true in you Kubernetes SecurityContext

In this episode of our Kubernetes Quick Hits video series, Eric Smalling–Sr. Developer Advocate at Synk– talks about privileged mode containers and why, for the vast majority of us, it’s simply a bad idea as well as some ideas for finding and preventing its use. Privileged mode is part of item number five from our recently published cheatsheet, 10 Kubernetes Security Context settings you should understand, check it out and start securing your Kubernetes application deployments today!
Vulnerability Management with Sysdig

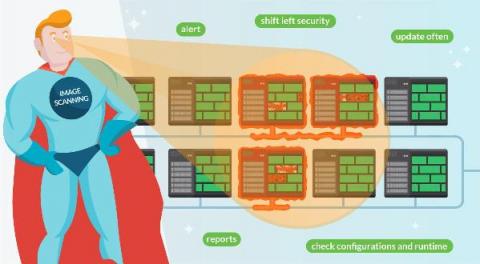
Software is always changing and improving, and within this process, developers can unknowingly introduce vulnerabilities. Discover how Sysdig Secure provides a single vulnerability management solution for both containers and hosts. It allows you to validate compliance across your whole infrastructure. And it's so easy to deploy, that you will be scanning images and hosts in seconds.

Top vulnerability assessment and management best practices

By implementing these vulnerability assessment and vulnerability management best practices you will reduce the attack surface of your infrastructure. We’re human, and many things we build aren’t perfect. That’s why we take our cars for a periodic inspection, or why we have organizations certifying that products are safe to use. Software is no different.

Get Kubernetes Backup - CloudCasa - in 1-Click from DigitalOcean Marketplace

Are you a DigitalOcean vendor or user and developing or deploying a Kubernetes application? You may want to preserve your cluster configuration, backup your persistent volumes to protect them from ransomware, accidental deletion, and long-term retention policies. CloudCasa is the only data protection and disaster recovery solution that has been tested and certified as a 1-Click appliction with DigitalOcean Kubernetes and available in their marketplace.

Threats targeting Kubernetes and Defences

Attackers are continuously evolving their techniques to target Kubernetes. They are actively using Kubernetes and Docker functionality in addition to traditional attack surfaces to compromise, gain required privileges and add a backdoor entry to the clusters. A combination of Kubernetes security and observability tools is required to ensure the cloud infrastructure monitoring and lockdown and to enable DevSecOps teams with the right tools for the job.

Securing Kubernetes workloads at Discover Financial Services

It’s a daunting task starting down the path to securing your workloads running on Kubernetes in the Cloud. There are no shortages of vendors with great tools in the Cloud security space. There is a multitude of domains that must be accounted for, along with internal challenges in bringing an organization along into new ways of thinking. This talk will focus on Discover’s Cloud security journey, with an overview of how the program has evolved over the last 4 years, key capabilities & concepts that have been embraced and challenges faced.

The Crossroad of Security & Observability in Kubernetes: A Fireside Chat

Security as an afterthought is no longer an option and must be deeply embedded in the design and implementation of the products that will be running in the cloud. It is increasingly more critical for many security teams to be almost, if not equally, knowledgeable of the emerging and rapidly evolving technology. Join Manish Sampat from Tigera, as explores the topic in detail with Stan Lee from Paypal.

Upgrading DevSecOps with compliance automation - Bryan Langston, Mirantis

Compliance automation is a commonly overlooked area of Kubernetes observability. The question is: how do you automate compliance to a security framework that isn’t well understood by DevSecOps teams to begin with? This lack of understanding contributes to mismanaged compliance efforts and in a worst-case scenario, audit exposures and organizational risk. This talk will walk through an example of how to 1) map compliance controls to specific Kubernetes technical configuration 2) automate the assessment of those controls 3) visualize the assessment results. DevSecOps teams will better understand how to incorporate compliance automation alongside security automation.