Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

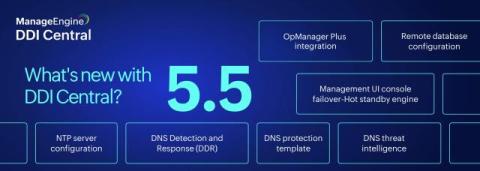
DDI Central 5.5 is here-with DNS threat intelligence, OpManager Plus integration, and more!

We’re excited to announce the launch of DDI Central version 5.5, a release shaped by the most demanded features from our customers and the ever-growing need for stronger security at the core of enterprise networks. With this version, the spotlight is on security, resiliency, and device-diagnostics driven IP address management.
Xalient appoints Andrew Critchley to accelerate Identity Strategy and Global Identity Managed Services

Xalient announces the appointment of Andrew Critchley as Head of UK Identity Practice and Global Identity Managed Services. Andrew is a recognized IAM Subject Matter Expert with a strong track record in developing and scaling identity services across global enterprises.

Reflecting on Wallarm's Journey: Growth, Resilience, and What Comes Next

When we started Wallarm, we focused on the APIs that power modern apps. We built an API-first platform, used AI from day one, and secured early patents in behavior-based detection and automated policy creation. The result: real-time, inline blocking with automatic API discovery that protects production, not just dashboards. Today’s investment isn’t only fuel for innovation—it’s proof of enterprise recognition.

Outpost24 Recognized as a Major Player in IDC MarketScape for Exposure Management

PHILADELPHIA (Aug 25, 2025) – Outpost24, a leading provider of exposure management solutions, today announced it has been named as a Major Player in the IDC MarketScape: Worldwide Exposure Management 2025 Vendor Assessment. The Outpost24 team believes this recognition underscores our comprehensive exposure management solutions and commitment to delivering exceptional customer service.

Securing AI Transformation: Why Cato Networks Acquired Aim Security

Every major technology wave reshapes enterprise security. The rise of the Internet gave us firewalls. The move to SaaS brought CASB and DLP. The migration to the cloud and rise of the hybrid workforce demanded a new architecture like SASE to enable network transformation. Today, the AI revolution is creating an entirely new attack surface – one that is as transformative as it is urgent.

Introducing Dynamic API Scanning

Application environments are more complex than ever, with APIs forming the critical connective tissue. But this proliferation has created a vast, often invisible, attack surface. Security teams are caught in a difficult position: compliance frameworks like PCI and SOC 2 demand API scanning, but offer little guidance. Meanwhile, you’re grappling with incomplete API inventories, and the market is a confusing mix of expensive, hard-to-instrument niche tools.

Introducing Astra's API Security Platform: See Every API, Secure Every Endpoint, Stop Breaches Before They Begin

APIs have quietly become the new first point of failure. They run the workflows your customers see, as well as the ones they never do. Every transaction, every authentication, every AI-driven feature is stitched together through APIs. That same interconnection has made them one of the most consistently underprotected parts of modern infrastructure. The numbers show the shift.

Breaking the Passkey Promise: SquareX Discloses Major Passkey Vulnerability at DEF CON 33

It is no secret that passwords are highly susceptible to phishing and brute force attacks. This led to the mass adoption of passkeys, a passwordless authentication method leveraging cryptographic key pairs that allows users to log in with biometrics or a hardware key. According to FIDO, over 15 billion accounts have been passkey-enabled, with 69% of users globally enabling passkeys in at least one account. The passkey promise is simple - eliminate passwords, eliminate vulnerabilities.