Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

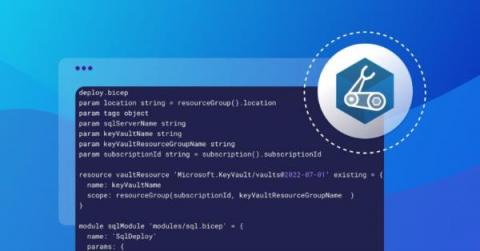
Azure Bicep security fundamentals

Azure Bicep is getting more popular by the day and is rapidly becoming the replacement for Azure Resource Manager (ARM) templates. In this post, I am going to go over some security fundamentals when using Bicep. If you are not familiar with Bicep then I recommend taking a look at the Microsoft Learn documentation to find out more.

GDPR Compliance for Email Marketing and Cold-Callings

Cold calling and emailing have always been popular and effective techniques of sales and communication with prospective clients. It is a way how brands can reach out to potential clients who may not be aware of your service or product offerings. It is a technique of creating brand awareness and lead generation. However, many customers see these activities as spamming.

2023 Cybersecurity predictions

Cybersecurity is a relatively new discipline in the realm of computing. Once computing became more democratized with PCs connected via local area networks (LAN) and client/server environments, adversaries quickly saw opportunities. The more democratized computing – the more risk and the potential for cyber adversaries. Dealing with cyber risk and adversaries is now part of a normal business plan.

Top 10 Cybersecurity Conferences of 2023

2023 is coming in hot. If you don't want to miss out on this year's best events, you better start planning your conference schedule early. To help you out, I created an overview of my personal top 10 favorite cybersecurity events in 2023 about application security, cloud security, IoT, and all the other topics that currently occupy the cybersecurity world.

Continued Exploitation and Evolution of ProxyShell Vulnerabilities - The Monitor, Issue 22

In August 2021, threat actors started to exploit ProxyShell vulnerabilities in certain Microsoft Exchange Server versions. Today, not only is Kroll seeing actors continue to leverage ProxyShell in larger network intrusions but also now organizations must also be on guard for the so-called ProxyNotShell vulnerabilities, which surfaced in September 2022.

Distraction on overdrive: Security in a time of permacrisis

We can probably all agree that we’re living in a state of permacrisis right now. After grappling with Covid-19, the world has been rocked by volatile stock markets, record-setting inflation, and the ongoing conflict in Ukraine. No wonder Collins Dictionary chose permacrisis as its word of the year for 2022.

Expel's Jon Hencinski: How to reduce risk through better security strategy

In this episode of The Future of Security Operations podcast, Thomas speaks with Jon Hencinski, Vice President of SecOps at Expel, a company with "a mission to make security easy to understand, easy to use, and easy to continuously improve." Jon is passionate about getting to the root cause of security issues and using strategy to help organizations eliminate problems.

Elastic + Tidal making MITRE ATT&CK easier

Security vendors seem to have a complicated relationship with the MITRE ATT&CK(™) matrix. With one hand, they hold it high as a powerful resource, and with the other, they criticize some aspect of it. But regardless of your viewpoint on any given day, ATT&CK is one of the most important resources for improving your understanding of threat capabilities and aligning those to technical controls, countermeasures, or mitigations.

Using LDAP Ping to Enumerate Active Directory Users

LDAP Nom Nom is a recently discovered brute-force technique for enumerating valid usernames in Active Directory — anonymously and without leaving any log entries behind. It abuses LDAP Ping, a little-known mechanism in Active Directory normally used by computers to check whether a domain controller is alive. This blog post explains how LDAP Ping works and how adversaries can abuse it with LDAP Nom Nom.