Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

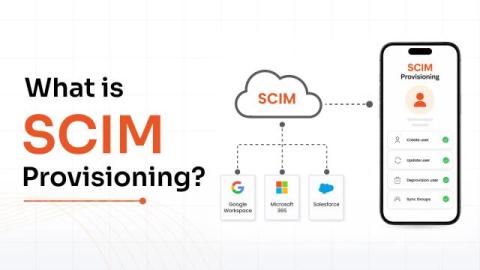
SCIM Provisioning: Complete Guide for IT Teams

Every time an employee joins your company, they need access to multiple systems. You can create accounts across 20+ different systems manually, which is time-consuming and error-prone. Or you can automate the entire user lifecycle with SCIM provisioning solution. Your admin team can save hours every week as accounts will be created, updated, and removed consistently. In this guide, you’ll understand what SCIM provisioning is, what its benefits are, and how you can implement it.
Security Debt Management Requires a Board-Level Conversation: Here's How to Own It

There is a version of security debt management that lives in a JIRA board. Tickets get filed, SLAs get set, and engineers work through the queue when they have capacity. It looks like a system. It functions like a pressure release valve — just enough motion to feel like progress, while the backlog quietly grows. That version is no longer adequate.

Protecting Sensitive Documents from Digital Threats

In our increasingly digital lives, we handle a vast number of documents, from personal financial statements and contracts to sensitive business reports. We often focus on securing our networks and devices, but the security of the documents themselves is frequently overlooked. Protecting these files from digital threats isn't just an IT department's problem; it's a personal responsibility for anyone creating, sharing, or storing information.
Featured Post

The biggest security risks facing financial institutions in 2026

Financial institutions are spending more on security than they were five years ago. They have more security tools, invest more in training, have more policies in place and report on security more regularly. That sounds positive, but it does not automatically make them more secure. One of the biggest challenges for security leaders is deciding where to focus. New vulnerabilities, threat reports and regulatory requirements appear all the time. With so much competing for attention, it can be difficult to separate genuine priorities from the latest headline.

Moving Overseas: Securing Your Assets During a Move

Moving to a new country brings a mix of excitement and massive logistical hurdles. Managing your money and protecting your hard-earned wealth during this transition requires immediate attention. Leaving your home country means adapting to new banking systems and different tax rules. You need a clear strategy to protect your bank accounts and physical property before boarding your flight. Taking the right precautions guarantees your wealth remains safe during the international relocation process.

Identity Verification Software: Why It Matters for Secure Digital Onboarding

As more financial services, lenders, fintech firms, and digital businesses move customer journeys online, identity verification has become a critical part of building trust. Customers expect fast onboarding, but organisations also need to prevent fraud, meet compliance obligations, and protect sensitive data. This is where identity verification software plays an important role. It helps businesses confirm that customers are who they claim to be while keeping the process efficient, secure, and user-friendly.

White-Label Link Building Agencies With the Shortest Turnaround Time

You told a client the backlinks would be live in three weeks. Your vendor just emailed to say the placement slipped again, and now you are the one writing the apology. Turnaround is the part of white-label link building that quietly decides whether your client renews or churns, and it is the part most providers are vague about.

Behind the Fake Tax Notice - Part II: ValleyRAT Unmasked

In Part I of this series — “Behind the Fake Tax Notice” — the Foresiet Threat Intelligence Team mapped a multi-country, tax- and invoice-themed phishing network built around hxxps://adresesvip/. That infrastructure, hosted on Alibaba Cloud in Hong Kong, was used to target taxpayers across India, Germany, Malaysia and Japan. The first report documented the lure, the sender and the hosting, but left one question open: what does the campaign actually deliver?

Why third-party risk management is broken, according to CISOs and analysts

Independent journalists, analysts, and working CISOs are all reaching the same conclusion about questionnaire-based, point-in-time risk assessment: it’s no longer enough. Risk and vulnerabilities keep growing, compliance obligations keep stacking up, and AI adds an entirely new surface to account for. CISOs need something better: a continuous approach with visibility across their business, that actually reduces risk rather than just documenting it.