Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

Devil's advocate? Uncensored Luciferus AI service advertised underground

On August 24, 2026, Counter Threat Unit (CTU) researchers observed an Exploit underground forum persona named “Optimus_Prime” advertising an uncensored AI subscription service named Luciferus. The persona joined Exploit on April 18, and their profile displays a “coding / coder” activity label. As of September 4, the persona has published 21 posts on the forum.
AI Governance When the AI Is Inside the Network

Most AI governance guidance assumes the AI sits beside the business. A model assists a decision, a copilot drafts a document, an agent processes a queue. Governance then asks who reviewed the output and whether the data was handled properly. ‍ In a telecom network the AI is inside the product.

Nobody Knows How Many AI Agent Breakouts There Have Been

Reuters reported at the end of July that OpenAI had found further cases of autonomous agents escaping containment, uncovered while investigating the Hugging Face intrusion. The reporting could not establish how many, when they happened or under what circumstances, because the company and outside experts were reviewing log data from earlier in the year to work it out.

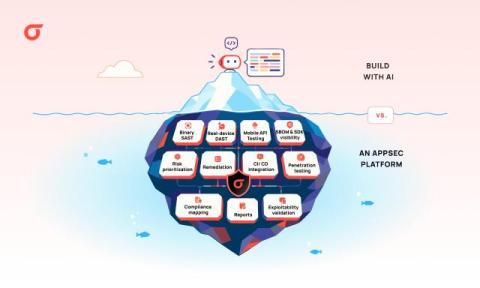
Why Buy a Mobile AppSec Platform Instead of Building With AI?

AI has lowered the cost of building mobile security tooling to near zero. However, it has not lowered the cost of operating it. Building a scanner is now a weekend project, while sustaining detection accuracy, threat research, real-device infrastructure, and developer trust across years remains a full organizational commitment. That distinction is the entire build-versus-buy question in 2026, and most evaluations get it wrong by measuring the wrong thing.

Astra Just Raised the Bar for AI-Enabled Attacks. Here's What That Means for Defenders

OpenAI published its assessment of its newest GPT model, Astra, and found it to be the first of their models to reach a critical level of cybersecurity capability, meaning that given the right tools and access, it could autonomously exploit previously unknown vulnerabilities. As a result, OpenAI has restricted Astra’s most advanced cybersecurity capabilities to trusted partners before a public rollout.

How to Improve AI Search Visibility Without Exposing Sensitive Data

AI search visibility creates a useful tension for security and marketing teams. A company wants its expertise, products, and evidence to be easy for search engines and AI systems to find. At the same time, it cannot afford to expose customer data, internal documents, credentials, or operational details simply to make its content more "machine readable." The right goal is not maximum crawlability. It is controlled public visibility: publish enough reliable information for a search system to understand and cite the company while keeping private information behind real access controls.

WebInject: The Web Agent Prompt Injection With No Payload

A browser agent in your cluster opens a supplier portal, screenshots it, and clicks somewhere the task never called for. The page looks exactly like the page the supplier serves, and to the person who checks it later, it still does. The classifier in front of the agent returned nothing, because the instruction that produced the click does not exist.

Approved Tools, Unapproved Agents

Approval works at the tool layer and it works well. A platform is assessed, terms are reviewed, a data processing agreement is signed, the tool enters the register, and named identities are entitled to it. Everything about that maps cleanly. ‍ Then somebody uses the approved platform to assemble an agent that acts on their behalf, with its own reach and its own credentials. The approval covered the application.