Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

AI Agent Governance Part 2 - What Good Looks Like: Governing AI Agents in Practice

If AI agents are becoming organizational actors, then governance needs to move beyond principles and into operational structure. In Camille Stewart Gloster’s upcoming book The Insider You Build, she explains that governance is not defined by policies or structures, but by whether it can actually influence system behavior at runtime. In an agentic environment, governance only exists where it can shape, constrain, and intervene in decisions as they happen.
Cosine Similarity Is Math, Not Magic

Cosine similarity is pure math. No magic. No understanding. Once you accept that, a lot of the confusion goes away. We talk to a lot of customers, and even seasoned engineers, who treat cosine similarity like magic that solves everything. Engineers talk about embeddings like they are definitive. Product teams trust similarity scores like they are facts. Vendors sell “semantic understanding” like the model actually understands. Truth is, it does not.

OWASP Top 10 LLM Risks Explained

As large language models (LLMs) become more embedded in business operations, the risks and attack methods targeting them are evolving just as quickly. The 2025 edition of the OWASP Top 10 for LLM Applications reflects this rapid evolution, addressing the current threats facing generative AI systems in production environments. For organizations investing in LLMs, understanding the risks is crucial for deploying these systems securely.

A2A vs MCP: Which Is More Secure?

Two protocols are shaping the AI revolution: A2A for agent-to-agent delegation, and MCP for agent access to tools and external systems. A2A expands who can participate in a workflow by enabling agent-to-agent delegation. MCP expands what agents can reach by connecting them to data and systems. By the end of 2026, task-specific AI agents are expected to appear in 40% of enterprise applications, up from less than 5% in 2025. That shift changes where security has to live.

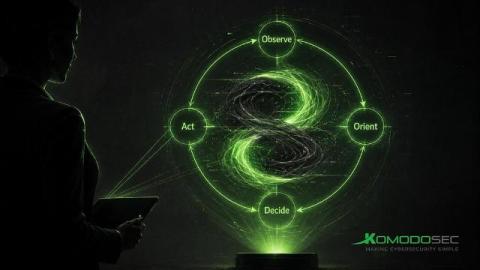
The Collapse of Symmetry: Why Periodic Pentesting is Strategic Suicide Against Algorithmic Warfare

The cybersecurity industry is sleepwalking. We are still captivated by the romanticized image of the hacker: a human in a hoodie manually typing code to breach a network. Wake up to the reality of 2026. The modern adversary is no longer human. It is algorithmic.

ITSP: Corelight launches Agentic AI that makes SOC triage 10x faster

Modern SOCs face a difficult reality: attackers are moving faster while analysts are being asked to investigate more alerts than ever. Learn how agentic triage helps security teams move from alert overload to evidence-backed investigations. Rather than relying on opaque AI outputs, the approach uses expert-written playbooks and exposes the underlying queries and evidence so analysts can verify conclusions against raw network data.

Charlotte AI AgentWorks: Build Your Security Workforce Demo

Today’s adversaries move at the speed of AI, so defenders need to reason, decide, and act faster across every stage of security operations. Meet Charlotte AI AgentWorks, a no-code agent builder that enables teams to create mission-ready AI agents directly inside the CrowdStrike Falcon platform.

Just vibe code it...

Sometimes unlimited tokens and rippin' guitar riffs can't solve every problem. The best builders know what NOT to build. Vibe coding might cut down on time, but that's only a fraction (20%) of the total software lifecycle cost. The other 70–80%? Maintenance, security patches, compliance updates. The slow grind of keeping it alive in production. When it comes to something as complex and critical as keeping your security airtight, depth wins over speed every time.

From PentestGPT to production: The state of AI-assisted offensive security with Charles Grandjean

Join us for this week's Defender Fridays as Charles Grandjean, CTO and Co-founder at Hexiagon AI, breaks down where AI-assisted pen testing actually stands today and what it means for both red teams and defenders. At Defender Fridays, we delve into the dynamic world of information security, exploring its defensive side with seasoned professionals from across the industry. Our aim is simple yet ambitious: to foster a collaborative space where ideas flow freely, experiences are shared, and knowledge expands.