Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

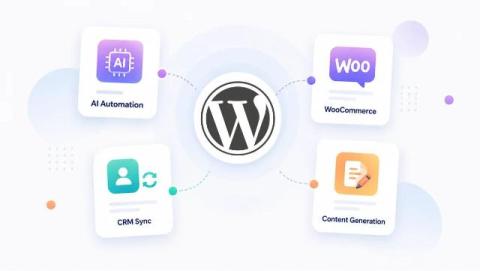
AI Agent for WordPress: The Complete 2026 Guide

In 1997, IBM’s Deep Blue, the first AI agent, made history by defeating Garry Kasparov at chess. Since then, AI agents have advanced dramatically, evolving from single‑task systems to agents like OpenAI’s Operator, which can autonomously fill out forms, place orders, and schedule appointments. WordPress is a popular CMS that powers more than 20% of the top one million websites. Bringing AI agents into WordPress opens up new possibilities, making sites more capable and adaptive.
Protegrity + Presidio: Secure Sensitive Data in AI Workflows

See how Protegrity and Presidio help developers secure sensitive data in AI workflows. This demo shows how Protegrity AI Developer Edition helps teams discover, protect, mask, and redact sensitive data before it reaches AI models, applications, or analytics pipelines. You’ll learn how developers can.

Acronis recognized in Info-Tech report: Why unified, AI-powered platforms are the future

The cybersecurity landscape is changing quickly, and independent research confirms what many organizations are already experiencing: Fragmented tools are no longer enough. A new Info‑Tech report, “Prioritize unified, AI-powered platforms for cybersecurity, data protection, endpoint management and compliance,” explores why leading organizations are rapidly shifting to unified platforms.

Stopping the Agentic Breach: How to Operationalize Your Defense Against Mythos-Speed Attacks

The industry has spent the past few weeks focused on Claude Mythos Preview and the rise of autonomous offensive AI. As outlined in Claude Mythos, Project Glasswing, and the Machine-Speed Security Race, this shift is not only about faster attacks. The same AI-driven acceleration that helps attackers discover weaknesses faster can also help defenders validate exposure sooner. For security operations teams, the challenge is turning that strategic shift into action.

Agentic AI Security: Governing Shadow Agents on Endpoints

Most enterprise security programs were built around a simple assumption, not invalid assumption that data moves when a person decides to move it. AI agents have broken that model, and now act autonomously, reading files, calling APIs, executing code, and transferring data across systems without waiting for a human to approve each step. Many of these agents were never sanctioned by IT or security.

Ep 44: You can't vibe code your way through a production outage

In this episode of Masters of Data, we tackle one of tech's buzziest debates: vibe coding versus production-ready software. We break down where AI-assisted "just make it work" coding genuinely shines (think POCs, prototypes, and getting stakeholder buy-in fast) and where it falls dangerously short when someone tries to ship it to ten thousand enterprise users. We also dig into David's agentic engineering workflow, security risks like malicious MCP servers and supply chain attacks, and why turning a vibe-coded prototype into real software still takes months, not days. Bottom line.

When AI changes the rules, attackers adapt

The dominant narrative around AI in security is one of emboldened defenders suppressing attackers. Yet, not everyone is convinced the future will be so rosy. In a recent Defender Fridays episode, Josh Neil, Co-founder and CTO of Alpha Level, made an argument that cuts against the celebratory mood: as AI makes known attack vectors harder to use, adversaries don't disappear. They adapt. For MSSPs and SOC teams, an adversary that looks like a user is a harder problem than one that looks like malware.

AI Agent Governance Part 1 - Beyond the Chatbot: Mastering AI Agent Governance

In 2024, we talked to AI. In 2026, AI is talking to our systems, our customers, and increasingly, acting on our behalf. With AI agents, we are moving AI from a tool to an actor, from assistance to agency and from outputs to actions. And that changes the nature of risk. AI agents plan, execute, and interact with the world on our behalf. They send emails, move data, trigger workflows, and increasingly operate across systems without human intervention.

Report: Adversarial Use of AI is Evolving

Threat actors are increasingly augmenting their attacks with AI tools, according to researchers at Google’s Threat Intelligence Group (GTIG). For the first time, GTIG observed a threat actor using a zero-day exploit developed by AI, although Google blocked the attack before it succeeded. Threat actors also continue to use Large Language Models (LLMs) for research, reconnaissance, and malware development.